Self-Managed Commerce 8.6.x Release Notes
Learn about changes to Self-Managed Commerce for this release. Fixes since the release are summarized in the changelog.
Changelog
The changelog contains the list of fixes and improvements made to Self-Managed Commerce 8.6 since its release date. To learn how to consume the updates, see Consuming Support Fixes.
| Commit | Description | Badges | Release Date |
|---|---|---|---|
| 8b54e2b5 | Upgraded the Google Guava library from 32.0.1 to 33.7.2 to address a high-severity security vulnerability (CVE-2026-102554). | Security | 5‑Nov‑2026 |
| 556c6e58 | Fixed a Cortex performance issue where api-platform was dispatching LINK and ADVISE operations to resource families already cached as not allowed. | Performance | 5‑Nov‑2026 |
| 6a1ce30a | Upgraded Tomcat from 9.0.122 to 9.0.123 to address CVE-2026-101356, CVE-2026-101296, CVE-2026-88041, CVE-2026-74049, CVE-2026-93446, CVE-2026-74048, CVE-2026-80353. | Security | 5‑Nov‑2026 |
| c6d90e3b | Build stability fix. | 3‑Nov‑2026 | |
| beba97c4 | Upgraded the PostgreSQL JDBC driver from 42.7.13 to 42.7.14 to address CVE-2026-107314 and CVE-2026-107315. | Security | 3‑Nov‑2026 |
| 48f9c7c1 | Fixed a performance issue with inefficient localized attribute key parsing by caching parsed results and eliminating repeated regex compilation per call. | Performance | 3‑Nov‑2026 |
| 93d8e5a1 | Build stability fix. | 3‑Nov‑2026 | |
| 2044e973 | Fixed an issue where Tomcat-based Commerce containers shut down immediately on SIGTERM, interrupting in-progress heap dumps instead of allowing the Java process to finish gracefully. | Build Tools | 29‑Oct‑2026 |
| d92eb067 | Fixed an issue where a malformed or unresolvable entry in extensions.json or plugins.json was silently ignored, causing all configured extension overrides to be discarded at startup. | 28‑Oct‑2026 | |
| 5f25cefe | Fixed an issue where a single failing or repeatedly duplicated search index notification could permanently stall the index update queue, causing indexes to go stale and eventually run out of memory during rebuilds. | Data model changes | 27‑Oct‑2026 |
| dbf30684 | Fixed a performance issue where the outbox message relay job lacked an optimized database index, causing inefficient queries against the outbox message table. | Performance Data model changes | 27‑Oct‑2026 |
| 01f2b97e | Upgraded Jackson from 2.22.3 to 2.22.4 to address three security vulnerabilities (CVE-2026-104895, CVE-2026-106554, CVE-2026-110879). | Security | 26‑Oct‑2026 |
| ecb60e56 | Search Server's in-memory cache entry limit is now capped during index rebuilds, preventing out-of-memory errors on large catalogs. | 26‑Oct‑2026 | |
| 58747dc3 | Removed and ban unused snappy-java 1.1.10.8 dependency to address CVE-2026-90559. | Security | 24‑Oct‑2026 |
| 3f2fc085 | Fixed an issue where concurrent reads of cached product attributes caused threads to spin indefinitely, driving CPU usage up until the service was restarted. | 23‑Oct‑2026 | |
| be4f3b0d | Updated the ActiveMQ container image to allow tuning ActiveMQ storeUsage and tempUsage limits and totals. Default values are set in the image but can be overridden with new container environment variables. | Build Tools | 23‑Oct‑2026 |
| d14321df | Fixed an intermittently failing deadlock retry integration test that could exhaust its retry budget due to a livelock, and added a missing error log when all retry attempts are exhausted. | 22‑Oct‑2026 | |
| a96981ce | Fixed an issue where upgrading across a major Lucene version permanently broke search indexes, causing all storefront and Commerce Manager searches to return no results. | 21‑Oct‑2026 | |
| 38944cec | Fixed an issue where orders with three or more partial captures against the same payment reservation failed with a duplicate key error, leaving orders partially charged and requiring manual intervention. | 21‑Oct‑2026 | |
| 7e0913b4 | The Operational Insights report now includes OpenJPA level 2 data caches alongside application caches, giving operators visibility into the memory footprint of the persistence cache tier. | 21‑Oct‑2026 | |
| 21e3c3ff | Removed msgpack-core dependency to address CVE-2026-90472. | Security | 21‑Oct‑2026 |
| cab0fde2 | Upgraded Logback from 1.6.3 to 1.6.5 and SLF4j from 2.0.18 to 2.0.19 to address CVE-2026-104721. | Security | 20‑Oct‑2026 |
| 1e5b8391 | Updated the Cortex Studio CSS compiler dependency to address 8 Javascript vulnerablilities. | 20‑Oct‑2026 | |
| 4f4e3ce7 | Fixed an issue where Commerce Manager failed to load extension classes that used the Log4j 2 API directly. | 15‑Oct‑2026 | |
| 9eb44f73 | @ResourceRepository and @ResourceService annotations can now be used in non-prototype classes such as permission parameter strategies without requiring a configurePrototypes workaround. | 15‑Oct‑2026 | |
| 32ecc416 | Fixed an issue where keyword searches with long multi-word phrases returned no results due to the search server rejecting queries that exceeded its maximum clause count. | Data model changes | 14‑Oct‑2026 |
| 277f4c83 | The Operational Insights Data Shape section now includes a record count for the index notification table (TINDEXNOTIFY). | 14‑Oct‑2026 | |
| 762cd555 | Fixed an issue where eight Cortex storefront resources evaluated every promotion rule twice per request, causing redundant pricing calculations when rendering cart totals, discounts, and applied promotions. | 14‑Oct‑2026 | |
| 1a245169 | Fixed an issue where the Search Server threw OutOfMemoryError during index rebuilds because queued index notifications were loaded entirely into memory before deletion. | 10‑Oct‑2026 | |
| 9bf70875 | Upgraded certified Java version from 17.0.18 to 17.0.20. | Security | 9‑Oct‑2026 |
| b9be5544 | Upgraded httpclient5 from 5.6.3 to 5.6.4 to address CVE-2026-71290. | Security | 7‑Oct‑2026 |
| 23479c48 | Fixed XML external entity injection vulnerabilities in the Import/Export module that allowed crafted import payloads to read server files or trigger outbound requests from the server. | Security | 7‑Oct‑2026 |
| a37c0da3 | Fixed multiple reliability issues in Operational Insights report generation. | 7‑Oct‑2026 | |
| 9ef93b5e | Replaced the unmaintained com.github.java-json-tools:json-schema-validator library with com.networknt:json-schema-validator 2.0.7 to resolve three security vulnerabilities (CVE-2026-86321, CVE-2026-86511, CVE-2026-86513). | Security | 7‑Oct‑2026 |
| e69a0cfe | Upgraded Extension Point Framework connectivity library build to Java 17. | Security | 6‑Oct‑2026 |
| f162abf5 | Upgraded Tomcat from 9.0.121 to 9.0.122 to address CVE-2026-86350, CVE-2026-77762, CVE-2026-78383, CVE-2026-75973, CVE-2026-78437, CVE-2026-73581, CVE-2026-77756. | Security | 6‑Oct‑2026 |
| c0a815b3 | Upgraded Jackson from 2.22.1 to 2.22.3 to address CVE-2026-83557, CVE-2026-19032, CVE-2026-68497, CVE-2026-89425, CVE-2026-89407, CVE-2026-91776, CVE-2026-91777. | Security | 1‑Oct‑2026 |
| 3c40112c | Fixed an issue where importing an order with a mixed-case store code failed with a foreign key violation. | 1‑Oct‑2026 | |
| a696dcc5 | Upgraded ActiveMQ from 5.19.10 to 5.19.11 to address CVE-2026-74761. | Security Build Tools | 1‑Oct‑2026 |
| 9efa7ba2 | Removed a redundant Tomcat version property from the extensions module to simplify Tomcat upgrades. | 1‑Oct‑2026 | |
| 87a40415 | Fixed an issue where Cortex permission checks bypassed a required pre-check and passed resource identifiers from unrelated resource types to parameter resolution strategies. | 28‑Sep‑2026 | |
| 8896d769 | Operational Insights cache sizing now uses a custom heap estimator that requires no JVM flags, replacing the previous engine that failed or silently under-reported on modern JVMs. | 24‑Sep‑2026 | |
| dfa89eb1 | Upgraded ant from 1.10.14 to 1.10.18 to address CVE_2026-78254. | 23‑Sep‑2026 | |
| 66cac275 | Upgraded the Node.js version used to build Cortex Studio from 6.x to 26.x. | 23‑Sep‑2026 | |
| f0d7c3da | Build stability improvements. | 22‑Sep‑2026 | |
| 5e295eda | Upgraded Zookeeper from 3.9.5 to 3.9.6 to address CVE-2026-79993, CVE-2026-59969, CVE-2026-59739, CVE-2026-84439, CVE-2026-84501. | Security | 22‑Sep‑2026 |
| fbd38540 | Fixed issue with a NullPointerException appearing in Operational Insights when the webapp smoketests were run. | 22‑Sep‑2026 | |
| c5f24d05 | Upgraded the certified MySQL 8.4 RDS version from 8.4.8 to 8.4.11. | 22‑Sep‑2026 | |
| 9bb42d23 | Upgraded the certified MySQL 8.0 RDS version from 8.0.43 to 8.0.46. | Security | 22‑Sep‑2026 |
| 16e2b686 | Upgraded the certified PostgreSQL 16 Amazon Aurora version from 16.10 to 16.14. | 21‑Sep‑2026 | |
| 48cb7ed8 | Cleaned up Cortex Studio npm dependencies by dropping unused packages and bringing package-lock.json back in sync with package.json. | 21‑Sep‑2026 | |
| e49ffde1 | Fixed an issue where completing a physical shipment paid with a retried charge incorrectly marks the order as failed and throws an unhandled exception. | 16‑Sep‑2026 | |
| 9b3a5bef | Fixed an issue where upgrading Logback to 1.6.x caused JLine stack traces to appear in the Cortex startup logs and silently broke colorised console output for local development. | 16‑Sep‑2026 | |
| a80b2823 | Upgrades jsoup from 1.15.3 to 1.23.2 to address CVE-2026-71497. | Security | 12‑Sep‑2026 |
| b732fffb | Upgraded Postgresql JDBC driver from 42.7.11 to 42.7.13 to address CVE-2026-54291. | Security | 12‑Sep‑2026 |
| ea359eb4 | Upgraded httpclient5 from 5.3.1 to 5.6.3 and httpcore5 from 5.2.4 to 5.4.3 to address CVE-2026-64607, CVE-2026-54399, CVE-2026-54428. | Security | 11‑Sep‑2026 |
| a26d6c1f | Upgraded Netty from 4.1.136.Final to 4.1.137.Final to address CVE-2026-75595 and CVE-2026-75596. | Security | 11‑Sep‑2026 |
| 38c3ae71 | Upgraded Logback from 1.5.35 to 1.6.3 to address CVE-2026-19880. | Security | 11‑Sep‑2026 |
| d917ca79 | Replaces the unmaintained org.fusesource.jansi:jansi 1.18 library with org.jline:jansi 4.3.1. | 11‑Sep‑2026 | |
| 852538bb | Removed the unused http-builder dependency from Cucumber test modules to eliminate a transitive dependency on a vulnerable version of commons-lang (CVE-2025-48924). | Security | 11‑Sep‑2026 |
| 30bc9f80 | Upgraded Tomcat from 9.0.120 to 9.0.121 to address multiple high-severity vulnerabilities. | Security | 8‑Sep‑2026 |
| 2836f4e4 | Fixed an issue where multiple Commerce Manager instances can claim and execute the same CSV import job concurrently, causing duplicate data. | Data model changes | 3‑Sep‑2026 |
| 08f331fc | Upgraded Apache ActiveMQ from version 5.19.6 to 5.19.10 to address 8 vulnerabilities with scores from 5.9 to 8.8. | Build Tools | 2‑Sep‑2026 |
| 1a0455ab | Fixed an issue where transacted JMS consumers open and tear down a real TCP connection to the ActiveMQ broker on every receive cycle, causing significant connection churn at idle and under load. | 1‑Sep‑2026 | |
| a6a02ad5 | Fixed an issue where MySQL upgrade tests on 8.5.x fail with a datetime truncation error caused by test price list assignments being created with a start date at or too close to the Unix epoch. | 31‑Aug‑2026 | |
| fca390e3 | Fixed an issue where Camel JMS request-reply (InOut) routes fail with an IllegalArgumentException after connection pooling changes removed a required connection factory property. | 28‑Aug‑2026 | |
| bc161863 | Fixed an issue where OpenID Connect token exchange requests send a malformed scope parameter, causing sign-in to fail with Microsoft Entra ID. | 27‑Aug‑2026 | |
| 6c9abee8 | Removed the unmaintained Natty date-parsing library from the test application to resolve a security vulnerability (CVE-2025-48924) in its transitive dependency on Commons Lang. | Security | 25‑Aug‑2026 |
| 267ab63f | Customer and shopper records for single-session (public) users are now created lazily, only when a cart or profile resource is accessed, rather than at token creation time. | Data model changes | 25‑Aug‑2026 |
| 56487481 | Build stability improvements. | 21‑Aug‑2026 | |
| eec34c1a | Updated the ActiveMQ container entrypoint to ensure signals reach the broker JVM process. | Build Tools | 21‑Aug‑2026 |
| 1b8e0f23 | Upgraded Logback from 1.5.32 to 1.5.35 to address CVE-2026-9828, CVE-2026-10532, and CVE-2026-13006. | Security | 20‑Aug‑2026 |
| 47ff3137 | Fixed an issue where importing a registered customer whose username already exists in the target store causes the entire import batch to fail with a raw duplicate key database error. | Data model changes | 20‑Aug‑2026 |
| ed14b19f | Fixed an issue where a Software Composition Analysis security scan falsely reports Bouncy Castle vulnerabilities by excluding unused Shiro crypto dependencies from the Maven dependency graph. | Security | 19‑Aug‑2026 |
| f502a159 | Upgraded Logback from 1.5.21 to 1.5.32 to address CVE-2026-1225. | Security | 18‑Aug‑2026 |
| ee8a3b5b | Fixed an intermittent cache eviction error during search indexing caused by several Ehcache cache key classes not implementing Serializable. | 18‑Aug‑2026 | |
| 39447be7 | Upgraded Log4j from 2.25.4 to 2.26.1 to address CVE-2026-49844. | Security | 18‑Aug‑2026 |
| 5184286e | Upgraded Jackson from 2.21.4 to 2.22.1 to address CVE-2026-59889, CVE-2026-54515. | Security | 17‑Aug‑2026 |
| 98100612 | Upgraded Netty from 4.1.135.Final to 4.1.136.Final to address CVE-2026-59901. | Security | 17‑Aug‑2026 |
| 457d928f | Fixed an issue where Selenium tests intermittently fail with a stale element reference error when calling click, doubleClick, or setChecked on a RAPTable row, resolved by adding retry logic to each method. | 17‑Aug‑2026 | |
| cda10981 | Parallelizes previously serial isolated Cucumber regression tests by scoping test data and configuration to unique stores, catalogs, and scenarios per test run, reducing pipeline duration by approximately 20–30 minutes. | 16‑Aug‑2026 | |
| 969b03d8 | Fixed a bug where transacted JMS routes built on CRSCEnabledRouteBuilder consume only one message and stall permanently, by removing the onCompletion hook that deadlocks the consumer thread on Camel 3 and later. | 15‑Aug‑2026 | |
| fda9760c | Fixed intermittent test failures where the ORDER_CREATED message assertion fails because the message is consumed before the listener is fully initialized. | 14‑Aug‑2026 | |
| 0b9094d9 | Fixed an issue where Cucumber test suites silently pass when step definitions are missing or unimplemented, by enabling strict mode across all 17 Java runners and 7 parallel runner templates. | 14‑Aug‑2026 | |
| ceebb402 | Fixed spurious "Unrecognized collection class" warnings logged by StrictDetachmentStrategyImpl in Cortex whenever an entity with a null collection-valued association is detached before caching. | 14‑Aug‑2026 | |
| dd0a2554 | Add missing storeTestPersister bean definition to fix AccountAssociates.feature. | 13‑Aug‑2026 | |
| 24e6ef6d | Upgraded Tomcat from 9.0.118 to 9.0.120 to address CVE-2026-59084, CVE-2026-59083, CVE-2026-55276, CVE-2026-53404, CVE-2026-55955, CVE-2026-55956. | Security | 13‑Aug‑2026 |
| 98180296 | Fixed a bug in Commerce Manager where saving a customer record after adding a new address caused the address to appear duplicated in the address list. | 11‑Aug‑2026 | |
| 61062dc2 | Build stability improvements. | 10‑Aug‑2026 | |
| a3889a95 | Fixed an issue where the coupon table migration generates random GUID values, causing the same coupon records to have different identifiers across environments, breaking data synchronization and import/export matching. | 10‑Aug‑2026 | |
| 63e1a098 | Fixed intermittent VirtualCatalog.feature failures by improving reliability of menu item widget interactions. | 9‑Aug‑2026 | |
| e1b85d05 | Refactored AccountAssociates.feature so its scenarios can run concurrently. | 9‑Aug‑2026 | |
| 89d33b7a | Added new RAPMenuItem test widget to standardize menu access in Selenium tests. | 7‑Aug‑2026 | |
| f755a4bf | Improves Commerce Manager Selenium test reliability by removing broken stale-element wait methods, consolidating redundant wait call stacks, introducing stale-safe RAP widget wrappers, and cleaning up dialog handling. | 7‑Aug‑2026 | |
| 40bf32ed | Fixed issue with Cortex Studio issuing a redundant GET request after a followlocation form POST. | 29‑Jul‑2026 | |
| 9de8a5b4 | Fixed incorrect @EqualsAndHashCode and @ToString annotations in the XPFDeliveryPolicy class. | 28‑Jul‑2026 | |
| 48d10ba6 | Removed unused Cortex bundles wrapped-spring-security-config, wrapped-spring-security-data, wrapped-spring-data-commons. | Security | 28‑Jul‑2026 |
| aacf84b6 | JMS message consumers now use dedicated, non-pooled connections instead of shared pooled connections, preventing consumers on low-traffic queues from becoming stranded when a broker connection fails silently. | 27‑Jul‑2026 | |
| 237033e7 | Adds a new downloadChecksumWithAlgorithm field to ops-spec.json for all four tool entries (Java, Maven, Tomcat, ActiveMQ), enabling vendor-published SHA-256/SHA-512 hashes to be used directly instead of manually calculated MD5 values. | Build Tools | 24‑Jul‑2026 |
| e84d0a90 | Fixed intermittent parallel Maven build failures with "Could not acquire write lock" on a cold local cache by increasing the artifact lock acquisition timeout from 30 to 120 seconds. | 24‑Jul‑2026 | |
| e0253994 | Upgraded Jackson from 2.21.2 to 2.21.4 to address CVE-2026-54513, CVE-2026-54512, CVE-2026-54516, CVE-2026-54514, CVE-2026-54517. | Security | 21‑Jul‑2026 |
| 1367cdbc | Operational Insights revenue metrics now only count completed orders, using the order completion date instead of the creation date, preventing historical revenue figures from changing retroactively. | 17‑Jul‑2026 | |
| b5a95b05 | Upgraded Spring Security from 5.8.15 to 5.8.16 to address CVE-2024-38827. | Security | 16‑Jul‑2026 |
| 1a4d0b4a | Upgraded Solr from 9.10.0 to 9.10.1 to address CVE-2026-22022. | Security | 15‑Jul‑2026 |
| 08020266 | Fixed issue with bundle price list cache using excessive memory due to holding entire ProductBundle in the cache key. | 14‑Jul‑2026 | |
| e0286447 | The promotion rule recompilation trigger interval has been reduced from 5 minutes to 10 seconds by default, and the delay and interval are now configurable via the ep.rule.compilation.delay and ep.rule.compilation.interval properties. | 13‑Jul‑2026 | |
| 1b5db14a | Upgraded Netty from 4.1.133.Final to 4.1.135.Final to address CVE-2026-45416, CVE-2026-50010, and CVE-2026-44249. | Security | 6‑Jul‑2026 |
| b3d957f2 | Upgraded Shiro from 1.13.0 to 2.2.1 to address CVE-2026-23901, CVE-2026-43828, and CVE-2026-49268. | Security | 3‑Jul‑2026 |
| f1d5ad05 | The Commerce Manager test-util module no longer uses PhantomJS to run JavaScript tests, fixing build failures on systems with OpenSSL 3.x (such as Debian Trixie); tests now run via HtmlUnit and JUnit. | 26‑Jun‑2026 | |
| 1b9faa84 | Upgraded certified Oracle version from 19.0.0.0.ru-2025-10.rur-2025-10.r1 to 19.0.0.0.ru-2026-01.rur-2026-01.r3. | Security | 26‑Jun‑2026 |
| 73b3b90a | Upgraded certified PostgreSQL version from 16.10 to 16.14. | Security | 26‑Jun‑2026 |
| c527a53c | Refactored ShoppingCart to include transient fields for selected payment instruments, to be consistent with how selected addresses and shipping options work. This also allows us to eliminate some database operations during checkout. | 22‑Jun‑2026 | |
| 81bca889 | Merchandisers can now switch an existing shopping cart promotion between no-coupon, public coupon, and private coupon activation modes without needing to recreate the promotion from scratch. | 17‑Jun‑2026 | |
| c6ac9b67 | Build stability improvements. | 10‑Jun‑2026 | |
| 525d5fa3 | Removed an obsolete reference to a non-existent method (getCurrentLupNumber) from the sync service merge filter configuration; this is a cleanup change with no functional impact. | 9‑Jun‑2026 | |
| 03b73f7e | Upgraded Netty from 4.1.130.Final to 4.1.133.Final to address CVE-2026-42583. | Security | 9‑Jun‑2026 |
| b6095702 | Upgraded SLF4j from 1.7.x to 2.0.x and Logback from 1.2.x to 1.5.x to address CVE-2024-12798, CVE-2024-12801 and CVE-2025-11226. | Security | 9‑Jun‑2026 |
| 7fa25ebb | Upgraded Log4j from 2.17.1 to 2.25.4 to address CVE-2026-34480, CVE-2026-34479, CVE-2026-34477. | Security | 9‑Jun‑2026 |
| b5358dbc | Upgraded Liquibase from 4.27.0 to 4.33.0 to address a bug with the latest PostgreSQL JDBC driver. | Security | 4‑Jun‑2026 |
| 9161d219 | Upgraded Postgresql JDBC driver from 42.4.4 to 42.7.11 to address CVE-2026-42198. | Security | 3‑Jun‑2026 |
| b64040af | Fixed issue with Cortex not producing logs in deployed environments after the Logback 1.5 upgrade. | 2‑Jun‑2026 | |
| 6b144da4 | Upgraded JJWT from 0.10.6 to 0.12.7 to address CVE-2024-31033. | Security | 1‑Jun‑2026 |
| 2dd3bef8 | Upgraded Tomcat from 9.0.117 to 9.0.118 to address CVE-2026-43512, CVE-2026-41284, CVE-2026-42498, CVE-2026-41293, CVE-2026-43513, CVE-2026-43515, CVE-2026-43514. | Security | 1‑Jun‑2026 |
| aee22f3a | Build stability improvements. | 1‑Jun‑2026 | |
| c007ec1c | A Liquibase changeset has been added to automatically run ANALYZE on PostgreSQL databases during each data population run, preventing query performance issues caused by missing table statistics after a major PostgreSQL version upgrade. | Performance | 26‑May‑2026 |
| 81811605 | Fixed an issue where promotion carrots were not displayed for products in a category referenced by a shopping cart promotion condition, caused by incorrect category GUID comparison logic. | 25‑May‑2026 | |
| 5d75878e | Fixed a bug where copying a promotion reused the original's selling context, causing changes to one promotion's shopper conditions to affect the other. A database migration script separates any previously affected promotions. | Data model changes | 21‑May‑2026 |
| 704d3a2d | Moved spring-tx bundle from bundles to bundles level 4 to prevent intermittent Cortex startup failure. | 17‑May‑2026 | |
| 9c55297b | Upgraded Apache ActiveMQ from version 5.18.7 to 5.19.6 to address CVE-2026-40466, CVE-2026-41044, and CVE-2026-39304. | Security | 17‑May‑2026 |
| 498337fe | Upgraded certified Oracle version from 19.0.0.0.ru-2025-07.rur-2025-07.r1 to 19.0.0.0.ru-2025-10.rur-2025-10.r1. | Security | 17‑May‑2026 |
| 7ae37a4a | Upgraded certified MySQL 8.4 RDS version from 8.4.6 to 8.4.8. | Security | 16‑May‑2026 |
| 55f45657 | Upgraded certified Aurora MySQL 8.0 version from 8.0.mysql_aurora.3.08.2 to 8.0.mysql_aurora.3.10.3. | Security | 16‑May‑2026 |
| 381734fd | Upgraded Jackson from 2.19.1 to 2.21.2 to address WS-2026-0003 (CVSS3 7.5), with SnakeYAML also upgraded from 2.4 to 2.5. | Security | 8‑May‑2026 |
| cdb35f3c | Automated ast-grep upgrade recipes have been added to assist customers in migrating customizations from version 8.5.x to 8.6.x, covering API renames, dependency changes, and cache name updates. | 7‑May‑2026 | |
| 2b54ac31 | Fixed issue in Commerce Manager where switching between "cart level" and "line item level" rules on an existing promotion did not show or hide the correct conditions and actions, which could cause unexpected behavior when saving. | 6‑May‑2026 | |
| 006470bb | Upgraded plexus-utils from 3.5.1 to 3.6.1 to address CVE-2025-67030 (CVSS3 score 9.8). | Security | 5‑May‑2026 |
| f2e05a63 | Fixed a memory inefficiency in StoreProductSkuFactoryImpl where cached StoreProductSku proxies unnecessarily retained a reference to the factory singleton. | 4‑May‑2026 | |
| b1ffbce5 | Updated handling of promotion category exclusions so that if the excluded category is a subcategory of the included category, products belonging to both the included and excluded category satisfy the condition. | 1‑May‑2026 | |
| 26c8ca01 | Improved Selenium test widgets: Fluent table-cell assertions, text-field clear, sharper retry classification in both retryAttempts and retryFunction. | 1‑May‑2026 | |
| 23af008f | Upgraded SOLR from 9.9.0 to 9.10.0 to address CVE-2025-12383 and CVE-2025-58457. | Security | 30‑Apr‑2026 |
| 98e69f53 | Resolved a race condition where simultaneous checkout requests for the same cart could cause a duplicate order constraint violation to be silently swallowed, resulting in a failure indicating that payment instruments are missing. | 29‑Apr‑2026 | |
| db497511 | Upgraded Tomcat from 9.0.116 to 9.0.117 to address CVE-2026-34487, CVE-2026-34486, CVE-2026-34483, and CVE-2026-34500. | Security | 28‑Apr‑2026 |
| 86937e14 | Fixed issue with inventory cache using excessive memory due to holding entire Product SKU in the cache key. | 25‑Apr‑2026 | |
| 13ff932f | Fixed intermittently failing Catalog Syndication integration tests. | 23‑Apr‑2026 | |
| f6a9c702 | Upgraded Zookeeper from 3.9.4 to 3.9.5 to address CVE-2026-24281 and CVE-2026-24308. | Security | 17‑Apr‑2026 |
| 0d39f6ce | Added missing distributionManagement to boms/pom.xml that was causing Maven deploy operations to fail. | 14‑Apr‑2026 | |
| 0d69ebd5 | Upgraded pf4j from 3.10.0 to 3.15.0 to address CVE-2025-70952. | Security | 10‑Apr‑2026 |
| 9c5c18e3 | Modified build parameters to remove ReservedCodeCacheSize 128m setting and use JDK default instead. | Build Tools | 9‑Apr‑2026 |
| c92a5a09 | Fixed maven-deploy-plugin configuration that was causing Maven deploy operations to fail. | 8‑Apr‑2026 | |
| b3be75f1 | Removed deprecated ServiceMix dependencies and replaced with wrapped bundles maintained by Elastic Path. | 8‑Apr‑2026 | |
| 1b3cf3dd | Updated Selenium tests to properly embed HTML source in reports. | 7‑Apr‑2026 | |
| e7e3e422 | Upgraded Tomcat from 9.0.110 to 9.0.116 to address CVE-2026-24734, CVE-2026-24733, and CVE-2025-66614. | Security | 7‑Apr‑2026 |
| 3cc2495c | Fixed intermittent failure in "Syndication Сategory flow tests: Create and then Delete Category, check ep.catalog JMS message, check created option projection via API" Cucumber test. | 3‑Apr‑2026 | |
| 94e09863 | Added assertColumnContainsExactly method to RAPTable class. | 3‑Apr‑2026 | |
| 391d4f7f | Added assertDoesNotContainRow method to RAPTable class. | 2‑Apr‑2026 | |
| 025b9cae | Improved Import/Export logging to show localized message instead of code for warnings and errors. | 2‑Apr‑2026 | |
| 57a9ed59 | Upgraded the EhCache servicemix version to make it consistent with the EhCache version. | Security | 1‑Apr‑2026 |
| 6d5c56b9 | Fixed test teardown issue in MergeEngineImplITest that can cause SyncToolLauncherMultipleExecutionsITest to fail. | 31‑Mar‑2026 | |
| 71140d95 | Additional fixes for "context has been closed" exceptions in batch named queries with list parameters when casting to OpenJPAQuery. | 31‑Mar‑2026 | |
| ce9bd00b | Updated Git configuration to ignore .claude folders. | 27‑Mar‑2026 | |
| 010683f6 | Upgraded Byte Buddy to version 1.18.4. | Security | 26‑Mar‑2026 |
| f4364bc6 | Fixed issue with Price List Assignment search in Commerce Manager not properly clearing the list when there are no search results. | 25‑Mar‑2026 | |
| c943b804 | Updated OpenID Connect functionality to support RFC-compliant cookie headers and avoid generating "Invalid cookie header" warnings. | 25‑Mar‑2026 | |
| db404621 | Data sync change to ensure that only changed values are updated in the target entities. This also ensures that products and skus are not reindexed when a new sku option value is added. | 24‑Mar‑2026 | |
| b18a3909 | Added retryAttempts() to Selenium test framework to safely nest retries inside retryFunction(). | 20‑Mar‑2026 | |
| 7be9985e | Additional fixes for "context has been closed" exception in Cortex when setting entity fields that were loaded from the cache. | 20‑Mar‑2026 | |
| 91565b5c | Fixed a race condition in Utils.uniqueCode() used during tests. | 19‑Mar‑2026 | |
| 96e430c6 | Added the ability to override the P2 repository locations. | Build Tools | 19‑Mar‑2026 |
| 84d5deeb | Upgraded certified Java version from 17.0.16 to 17.0.18. | Security | 16‑Mar‑2026 |
| b923fb8f | Updated Payment Configuration Cucumber tests to generate new stores and prevent intermittent failures when running tests concurrently. | 13‑Mar‑2026 | |
| c13dcc57 | Fix for intermittent "context has been closed" exception in Cortex when accessing fields of bundle constituent products or product SKUs. | 12‑Mar‑2026 | |
| 11b26e69 | Upgraded rhino from 1.7.7.2 to 1.7.14.1 to address CVE-2025-66453. | Security | 12‑Mar‑2026 |
| c0ce2993 | Upgraded okhttp from 3.14.1 to 4.12.0 to address CVE-2021-0341. | Security | 12‑Mar‑2026 |
| eef8d95d | Improved Selenium test reliability and maintainability by introducing typed widget APIs that query the widget model directly, replacing brittle CSS selectors with strict element assertions, automatic retry on transient errors, and session cleanup. | 10‑Mar‑2026 | |
| 77b3de9e | Fixed bug with Abandoned Cart Cleanup job deactivating the wrong shopping carts. | 5‑Mar‑2026 | |
| ed9e26d3 | Fixed issue with descender characters (g, p, y, j, q) being cut off in Commerce Manager table headings. | 4‑Mar‑2026 | |
| bbe26585 | Fixed multiple bugs with promotion exception logic and reverted behaviour change of the "cart contains category" promotion condition done in a previous patch. | 27‑Feb‑2026 | |
| a6613e13 | Added cleanup job to delete shopping cart line items that are soft deleted. | 23‑Feb‑2026 | |
| 7fd6fa15 | Upgraded AssertJ from 3.11.1 to 3.27.7 to address CVE-2026-24400. | Security | 18‑Feb‑2026 |
| e1421601 | Fixed null pointer exception that can occur when retrieving inventory details for a bundle with no constituents. | 12‑Feb‑2026 | |
| e983a3c2 | Removed the runAlways flag off of the FK-BATCH Liquibase changesets to avoid creating repeat DATABASECHANGELOG entries in the database. | Data model changes | 10‑Feb‑2026 |
| fd6a7916 | Added new with-snapshot-api-platform and with-snapshot-ep-xpf-spi profiles for building with development versions of these dependencies. | 5‑Feb‑2026 | |
| 86ff431a | Fixed bug in which removing an attribute from a product type causes all attribute values to be deleted (instead of just the ones for products/skus assigned to that product type). | 3‑Feb‑2026 | |
| 1c27e8e2 | Upgraded msgpack-core from 0.8.13 to 0.9.11 to address CVE-2026-21452. | Security | 2‑Feb‑2026 |
| 01837c17 | Adds a new com.elasticpath.logging JMX endpoint to all Self-Managed Commerce services. This allows you to modify the log levels of running services in real time. | 2‑Feb‑2026 | |
| f1917e0e | Added support for custom headers in Cortex Studio. | 2‑Feb‑2026 | |
| f2790983 | Improved reliability of WebDriver management in Selenium tests. | 29‑Jan‑2026 | |
| 07678518 | Cleaned up EmailStepDefinitions by removing inappropriate TestExecutionListeners. | 29‑Jan‑2026 | |
| f0794b3d | Fixed intermittent failures in Performance Insights tests caused by resetting the database between each test. | Performance | 28‑Jan‑2026 |
| e10dce2c | Improved reliability of search-related Commerce Manager test steps to avoid race conditions. | 27‑Jan‑2026 | |
| 4649a676 | Removed Felix webconsole dependency from ext-cm-webapp. | 26‑Jan‑2026 | |
| b92495ca | Fix for intermittent context has been closed exception in Cortex under high load. | 26‑Jan‑2026 | |
| 5c5b3098 | Fixed skipITests and skipCucumberTests properties not skipping some expected modules. | 26‑Jan‑2026 | |
| 131c706c | Fixed issue causing Order Cleanup jobs to fail when order has associated order holds. | Data model changes | 14‑Jan‑2026 |
| 32522be8 | Added more detail to assertion output when Cortex Cucumber step definitions fail. | 13‑Jan‑2026 | |
| 06750c0c | Allow IntelliJ to properly resolve Eclipse Remote Application Platform dependencies in Commerce Manager classes. | 13‑Jan‑2026 | |
| bf0defcf | Updated Commerce Manager to allow attribute value editor to be opened when product, SKU, or category is locked in changeset mode. | 12‑Jan‑2026 | |
| f9b8a787 | Refactored confusing Amount of transaction should be (.*) Selenium test definition. | 7‑Jan‑2026 | |
| f164caa6 | Fixed intermittently failing Pre/Back-Order Cucumber tests. | 7‑Jan‑2026 | |
| 6b047c1f | Added the ability to set and distinguish between present and not present boolean customer attribute values in Commerce Manager. | 7‑Jan‑2026 | |
| 4337b4ec | Removed zoom graph builder functionality in Cortex Studio. | Security | 7‑Jan‑2026 |
| 85fa870a | Updated protobuf-java version from 3.16.3 to 3.25.5 to address CVE-2024-7254. | Security | 6‑Jan‑2026 |
| 65d19d78 | Upgraded certified Oracle version from 19.0.0.0.ru-2025-01.rur-2025-01.r2 to 19.0.0.0.ru-2025-07.rur-2025-07.r1. | Security | 19‑Dec‑2025 |
| 1892845c | Fixed Selenium test issue causing Multiple elements (2) found for selector: div[widget-id*='Sh'][appearance-id='ctab-item'][seeable='true'] warnings in the logs. | 18‑Dec‑2025 | |
| 2aa44e81 | Upgraded certified MySQL RDS version from 8.4.5 to 8.4.6. | Security | 17‑Dec‑2025 |
| f018dda5 | Added support for MySQL 8.4 in Build Tools. The default MySQL version that gets built by the build_base_images.yml playbook is now 8.4. | Build Tools | 16‑Dec‑2025 |
| f28a50a5 | Upgraded certified PostgreSQL version from 16.9 to 16.10. | Security | 8‑Dec‑2025 |
| 5d627fed | Updated coupon service to ensure that whitespace is trimmed when new coupon codes are created. | 5‑Dec‑2025 | |
| 958fb289 | Fixed potential date truncation error during Search Server startup that prevents promotion rule compilation. | 4‑Dec‑2025 | |
| 4a70d245 | Fixed AbstractPageObject#clearAndTypeText to improve detection that ensures that the field text was correctly entered. | 28‑Nov‑2025 | |
| d9289f6c | Upgraded certified MySQL 8.0 RDS version from 8.0.41 to 8.0.43. | Security | 28‑Nov‑2025 |
| 85b2d665 | Fixed issue where Java compiler warnings would fail build but not show the reason unless the fork configuration was removed. | 28‑Nov‑2025 | |
| 22533ae1 | Upgraded jQuery UI from 1.11.4 to 1.13.2 to fix autocomplete UI issue in Cortex Studio. | Security | 22‑Nov‑2025 |
| 9207c9ef | Replaced ruleUpdate.properties and catalogPromo.properties files written by the Search Server with a new TJOBEXECUTION database table. | Data model changes | 22‑Nov‑2025 |
| 2ba36614 | Fixed incorrect payment API response error message when refund fails. | 21‑Nov‑2025 | |
| dbb2d048 | Fixed an intermittent failure in Create Catalog Selenium tests. | 19‑Nov‑2025 | |
| 7faa5f2a | Fixed issue in which a new master catalog with all languages configured could not be opened in Commerce Manager. | 19‑Nov‑2025 | |
| 18c4559a | Improved how Checkstyle rules are defined to use suppression files for Integration Tests. | 17‑Nov‑2025 | |
| 80bfd2ed | Fixed NullPointerException that can occur in Import/Export API when import fails. | 12‑Nov‑2025 | |
| e80357d4 | Fixed refund error that can occur if the order payment events include reverse charges. | 12‑Nov‑2025 | |
| f751a987 | Fixed issue where the JaCoCo test coverage Maven plugin was not executing. | 10‑Nov‑2025 | |
| 56e8f78d | Fixed multiple issues related to null or blank customer profile attribute values. | 10‑Nov‑2025 | |
| f9aed82d | Upgraded Zookeeper from 3.9.3 to 3.9.4 to address CVE-2025-58457. | Security | 7‑Nov‑2025 |
| 1b4fd522 | Updated attributeByUidCache cache max entries from unlimited to 10,000 in ehcache-fast-updates.xml. | 7‑Nov‑2025 | |
| d39975de | Ensure that Checkstyle verifies JavaDocs for all public, protected, and package private methods. | 6‑Nov‑2025 | |
| df32c164 | Upgraded Tomcat from 9.0.107 to 9.0.110. | 6‑Nov‑2025 | |
| ebdfc146 | Fixed issue where the applied line item discount amount could exceed the line item subtotal if multiple promotions are stacked. | 4‑Nov‑2025 | |
| f32a7696 | Set default maxThreads for all services to 250 to match Operational Insights recommendations. | Build Tools | 3‑Nov‑2025 |
| 2a4f5745 | Upgraded dependencies within Fluent RelOS Client to address CVE-2025-48924. | Security | 30‑Oct‑2025 |
| 763dad66 | Upgraded fsevents from 1.2.8 to 1.2.11 to address CVE-2023-45311. | Security | 29‑Oct‑2025 |
| d19b2eb2 | Fixed intermittent failures in "Shipment line item contains tax" Cucumber test due to a race condition. | 29‑Oct‑2025 | |
| b436f609 | Fixed comment on releaseShipmentTrigger cron expression. | 28‑Oct‑2025 | |
| 80575efe | Modified XPFTaxableShoppingItem so cart tax calculation results are reusable at checkout by the ElasticPathTaxCalculator cache. | 23‑Oct‑2025 | |
| 57b3af50 | Added comments and improved the input validation in the ActiveMQ container entrypoint script. | Build Tools | 22‑Oct‑2025 |
| a5dc0b1b | Updated certified Java version from 17.0.7 to 17.0.16. | 22‑Oct‑2025 | |
| c0b94459 | Added a new index to TCOUPONUSAGE to improve performance for the query to find automatically applied coupons. | Performance Data model changes | 21‑Oct‑2025 |
| ed33481b | Fixed product reindexing issues after updating sku option values in a catalog. | 21‑Oct‑2025 | |
| 7d813dc3 | Switched default detachment strategy from strict to non-detaching to avoid 'this.pcStateManager is null' exceptions while importing in the Import/Export API. | 21‑Oct‑2025 | |
| 1f80fe03 | Upgraded Jetty from 10.0.24 to 10.0.26 to address CVE-2025-5115. | Security | 21‑Oct‑2025 |
| 95b49a76 | Upgraded jakarta.mail from 1.6.7 to 1.6.8 to address CVE-2025-7962. | Security | 17‑Oct‑2025 |
| c471ac66 | Added new configuration query parameter to the Import/Export API to allow clients to select different import configuration files to use for the import. | 9‑Oct‑2025 | |
| 684fa02c | Resolved the localized message key: incompatible-configuration warnings during service startup. | 2‑Oct‑2025 | |
| 0c43b69c | Fixed checkout failure that can occur when resubmitting a shopping cart that previously had a payment issue. | 30‑Sep‑2025 | |
| 8ea8995d | Upgraded Apache Solr from 9.8.0 to 9.9.0 to address CVE-2024-51504. | Security | 24‑Sep‑2025 |
| fee0460a | Upgraded Checkstyle plugin from version 2.17 to 3.6.0. | Security | 24‑Sep‑2025 |
| 99889b4d | Fixed exception that occurred when copying a cart promotion with rule exceptions defined. | 23‑Sep‑2025 | |
| 16329baf | Enabled Checkstyle and PMD checks in webapp-smoketests module. | 23‑Sep‑2025 | |
| 24013d71 | Enabled Checkstyle and PMD checks in ext-mock-services module. | 23‑Sep‑2025 | |
| 6e4c9ee7 | Upgraded netty-handler from 4.1.118.Final to 4.1.125.Final to address CVE-2025-58057. | Security | 22‑Sep‑2025 |
| c0af1c95 | Fixed issues running reset-db on a local Oracle database. | 18‑Sep‑2025 | |
| 5037860d | Fixed load.sh/unload.sh/replace.sh scripts generated by the Maven Archetype when creating an external plugin so that they work properly with the new cargo-based service startup mechanism. | 17‑Sep‑2025 | |
| d0caa7da | Upgraded certified PostgreSQL version from 16.6 to 16.9. | Security Data model changes | 17‑Sep‑2025 |
| f511dfb5 | Fixed data type issues with TRMAGENERATOR and TORDERNUMBERGENERATOR that required the database to workaround through implicit casts. | Data model changes | 16‑Sep‑2025 |
| 98d1c736 | Fixed issue with Search Server taking up to an hour to process index update notifications by reducing the query cache timeout from 1 hour to 5 seconds. | 15‑Sep‑2025 | |
| 87501f2b | Fix for potential "Value not present" error in Cortex if a new sku option value is added and assigned to a new product SKU before the sku option cache expires. | 12‑Sep‑2025 | |
| 93fefdd8 | Fixed an issue in the data-pop tool container entrypoint script where files from a secure-configuration repository were being ignored and not applied. | 12‑Sep‑2025 | |
| 17d27c0b | Added new cortex.headers.ignore JVM parameter that instructs Cortex to ignore the specified headers. | 11‑Sep‑2025 | |
| cf84fea5 | Changed the behaviour of the "cart contains category" promotion condition so that exclusions only override categories that are explicitly included. | 11‑Sep‑2025 | |
| 87abe894 | Fixed "Error during type conversion" exception that appeared in Integration Server logs after each Export API request. | 5‑Sep‑2025 | |
| a14369d5 | Updated the ext-container-layout project to include the same assembly rules used in the ext-deployment-package project, specifically so builds will fail if artifacts don't exist. | 5‑Sep‑2025 | |
| a7738796 | Upgraded commons-lang from 3.10 to 3.18.0 to address CVE-2025-48924. | Security | 4‑Sep‑2025 |
| 3ec39744 | Changed "No product was found for base amount" error to a warning. | 4‑Sep‑2025 | |
| 02d5610b | Upgraded Camel from 3.21.5 to 3.22.4 to address CVE-2025-29891 and CVE-2025-27636. | Security | 4‑Sep‑2025 |
| 7f99fe6e | Modified XPFTaxableShoppingItem so that its GUID matches the shopping cart line item GUID, so that the ElasticPathTaxCalculator cache doesn't miss on subsequent identical tax lookups. WARNING: Make sure to consume patch 0c43b69c at the same time as this patch to avoid potential checkout failures. | 2‑Sep‑2025 | |
| 2f363c78 | Upgraded nimbus-jose-jwt from 9.37.2 to 10.2 to address CVE-2025-53864. | Security | 2‑Sep‑2025 |
| ae6093ff | Fixed issue with service level options in the Commerce Manager promotion actions not updating correctly after the selected stores are changed. | 21‑Aug‑2025 | |
| 91085e30 | Removed all ESAPI dependencies, which were not effectively protecting the Cortex API endpoints and were including vulnerable transitive dependencies. | 21‑Aug‑2025 | |
| 8b6cafe8 | Replaced all uses of deprecated org.osgi.core and org.osgi.annotation dependencies with osgi.core and osgi.annotation. | 12‑Aug‑2025 | |
| 166460e5 | Fixed issue on promotion editor where store and catalog assignments were not persisted if changed after an initial save. | 11‑Aug‑2025 | |
| 6264ddc6 | Fixed duplicate guid in facet test data that was causing intermittent test failures. | 31‑Jul‑2025 | |
| 16aa1f55 | Upgraded ActiveMQ from 5.18.5 to 5.18.7 to address CVE-2025-27533. | Security | 31‑Jul‑2025 |
| 3b041842 | Fixed connection leak in DBConnector classes. | 28‑Jul‑2025 | |
| e8648705 | Upgraded Jackson from 2.16.1 to 2.19.1 and switched to jackson-bom to define dependency versions. | Security | 23‑Jul‑2025 |
| 5ad1bc9e | Fixed the Build Tools script build_source_tree.sh to properly handle the --deploy command-line argument. | Build Tools | 22‑Jul‑2025 |
| 1f67e6cf | Added a new COMMERCE/STORE/FILTEREDNAVIGATION/priceFacetingEnabled setting that controls whether price faceting support is enabled. If disabled, product search indexing may be significantly faster. | Performance Data model changes | 22‑Jul‑2025 |
| f13ddde7 | Upgraded Tomcat from 9.0.106 to 9.0.107. | Security | 18‑Jul‑2025 |
| 954c43fd | Fixed all @Named annotations that are paired with @Autowired to the correct @Qualifier annotation. | 18‑Jul‑2025 | |
| e8f093ee | Fixed potential race condition for limited use coupons when incrementing the coupon usage count during checkout, causing some uses to be missed. | 17‑Jul‑2025 | |
| 93138090 | Fixed multiple incorrect XML bean configurations. | 17‑Jul‑2025 | |
| 1b4202c2 | Updated both the Build Tools build container image and the Build Tools application container base images to Amazon Linux 2023.7.20250623.1. | Build Tools | 15‑Jul‑2025 |
| 81a6297d | Fixed error that was occurring on the Commerce Manager exchange wizard after modifying items to be exchanged. | 11‑Jul‑2025 | |
| 55e7656f | Fixed issue where resending a Gift Certificate for a specific order line item was resending all order gift certificates to the specified recipient. | 10‑Jul‑2025 | |
| b1af4e5c | Added support for IS NULL and IS NOT NULL to EP Search Query Language. | 10‑Jul‑2025 | |
| 96d76d33 | Upgraded commons-beanutils from 1.9.4 to 1.11.0. | Security | 9‑Jul‑2025 |
| 6226ed30 | Added a new warning to the logs when a service using SwitchableProxyBinder is using the fallback implementation, which usually indicates that application-level caching is not working. | 9‑Jul‑2025 | |
| 381ed781 | Upgraded Tomcat from 9.0.105 to 9.0.106. | Security | 8‑Jul‑2025 |
| 683c10ca | Upgraded spring-security from 5.8.14 to 5.8.15. | Security | 8‑Jul‑2025 |
| 06f76ed4 | Fixed issue with the simulated selling context dialog in Commerce Manager in which labels were not appearing. | 8‑Jul‑2025 | |
| 97cd0113 | Fixed infinite recursion bug in CacheableFacetService#findAllFacetsForStore. | 8‑Jul‑2025 | |
| c05dd186 | Modified bundle availability logic so that bundles appear as available as long as sufficient constituents are available to satisfy the bundle selection rules. | 7‑Jul‑2025 | |
| 0dc0da93 | Fixed parsing of queries in LuceneRawQueryComposerImpl that was causing problems for the search server when processing some index notifications. | 27‑Jun‑2025 | |
| e4229c02 | Build Tools: Set timeouts for Maven commands, so that Maven builds triggered by these tools will fail fast if Maven artifact download connections hang. | Build Tools | 25‑Jun‑2025 |
| 9c50ae15 | Fixed an issue where domain events are not always triggered as expected if the domain class has been extended. | 24‑Jun‑2025 | |
| 637a79b4 | Certified MySQL RDS 8.4. | 24‑Jun‑2025 | |
| f3f43041 | Fixed the Operational Insights revenue calculations to exclude failed but include cancelled orders. | 24‑Jun‑2025 | |
| b08a2bad | Fixed issue in which the CM_USER_CREATED event is sent before the Commerce Manager user is persisted. | 21‑Jun‑2025 | |
| b89551b3 | Build Tools: Updated the ActiveMQ container's entrypoint.sh script to enable new ActiveMQ container configuration options. Users can set new environment variables EP_ACTIVEMQ_X_JVM_ARGS and MAXIMUM_CONNECTIONS. | Build Tools | 20‑Jun‑2025 |
| 217d9b5c | Added a new ext-container-layout module with updated build tools, to simplify building Self-Managed Commerce container images. | 20‑Jun‑2025 | |
| ea48517e | Fixed issue that causes search indexing to fail if multiple attribute values exist for the same attribute with the same locale. | 19‑Jun‑2025 | |
| 943a1104 | Minor cleanup of code around Extension Point Framework event-based extensions. | 18‑Jun‑2025 | |
| 79f8124b | Replace the unmaintained tag library taglibs-standard-impl with the newer jakarta.servlet.jsp.jstl. | Security | 16‑Jun‑2025 |
| 1bacbb36 | Upgraded Tomcat from 9.0.102 to 9.0.105. | Security | 12‑Jun‑2025 |
| 20bc33c7 | Fixed SQL Injection issues identified by Static Application Security Testing tooling in ep-persistence-openjpa. | Security | 5‑Jun‑2025 |
| f0b6086b | Upgraded jetty-server from 9.4.56.v20240826 to 9.4.57.v20241219. | Security | 5‑Jun‑2025 |
| 418d58fe | Fixed suppression for false positive FindBugs issues. | Security | 5‑Jun‑2025 |
| 6883bca6 | Fixed multiple issues with limited usage promotions: Promotion wizard not saving the flag, error occurring when checking out, and a potential race condition during checkout. | Data model changes Requires downtime | 5‑Jun‑2025 |
| ff11c3ea | Added calls to super.configure() within configure methods of route builders extending CRSCEnabledRouteBuilder. | 2‑Jun‑2025 | |
| a9e8f450 | Build stability improvements. | 30‑May‑2025 | |
| 8eaaffa7 | Fixed issue that was sending messages to VirtualTopic.ep.catalog containing an error message when Catalog Syndication was triggered. | 29‑May‑2025 | |
| 3313cbbe | Fixed issue with Extension Point Framework entities missing all non-localized attribute values when a localized attribute contains a non-localized fallback value. | 27‑May‑2025 | |
| bcd7a680 | Made ordering of payment method elements consistent in Cortex. | 26‑May‑2025 | |
| f8a7ee2a | Multiple conflicting jars: com.github.java-json-tools:json-schema-core:1.2.14, com.github.java-json-tools:json-schema-validator:2.2.14 | 21‑May‑2025 | |
| 4b4ffe35 | Added optional JUnit 5 support to the platform. | 20‑May‑2025 | |
| 9a410dc8 | Multiple conflicting jars: com.sun.activation:jakarta.activation:1.2.2, com.sun.activation:javax.activation:1.2.0, jakarta.activation:jakarta.activation-api:1.2.2, javax.activation:activation:1.1 | 20‑May‑2025 | |
| db02b7f6 | Multiple conflicting jars: aopalliance:aopalliance:1.0, org.glassfish.hk2.external:aopalliance-repackaged:3.1.1, org.springframework:spring-aop:5.3.39 | 19‑May‑2025 | |
| 1c7f4991 | Multiple conflicting jars: com.antkorwin:xsync:1.3, org.hibernate.validator:hibernate-validator:6.2.0.Final | 19‑May‑2025 | |
| 4081d2eb | Multiple conflicting jars: javax.el:javax.el-api:3.0.0, org.glassfish:jakarta.el:3.0.4 | 18‑May‑2025 | |
| 62f673c2 | Multiple conflicting jars: io.swagger.core.v3:swagger-annotations-jakarta:2.2.22, io.swagger.core.v3:swagger-annotations:2.1.13 | 17‑May‑2025 | |
| 4cc9ecce | Multiple conflicting jars: jakarta.xml.bind:jakarta.xml.bind-api:2.3.3, javax.xml.bind:jaxb-api:2.3.1 | 16‑May‑2025 | |
| 749883b6 | Multiple conflicting jars: jakarta.validation:jakarta.validation-api:2.0.2, javax.validation:validation-api:2.0.1.Final | 16‑May‑2025 | |
| b696b384 | Fix for banned dependency errors introduced by "Multiple conflicting jars: org.slf4j:jcl-over-slf4j:1.7.32, org.springframework:spring-jcl:5.3.39, commons-logging:commons-logging:1.1.1" | 15‑May‑2025 | |
| 6b7cb213 | Added debug logging for SwitchableProxyBinder. | 15‑May‑2025 | |
| 1ca4e9bf | Multiple conflicting jars: org.slf4j:jcl-over-slf4j:1.7.32, org.springframework:spring-jcl:5.3.39, commons-logging:commons-logging:1.1.1 | 15‑May‑2025 | |
| ceb1bb00 | Multiple conflicting jars: javax.servlet:javax.servlet-api:3.1.0, org.eclipse.jetty.toolchain:jetty-servlet-api:4.0.6 | 15‑May‑2025 | |
| dbc2b7c7 | Multiple conflicting jars: com.sun.mail:imap:1.5.6, com.sun.mail:jakarta.mail:1.6.7, com.sun.mail:javax.mail:1.5.6 | 15‑May‑2025 | |
| 8288ad77 | Refactored b2b-buyer-functionality.feature to use client.authRegisteredUserByName instead of JWT authentication. | 12‑May‑2025 | |
| d80268af | Upgraded certified MySQL 8.0 Aurora version from 8.0.mysql_aurora.3.04.2 to 8.0.mysql_aurora.3.08.2. | Security | 11‑May‑2025 |
| c5a78213 | Fixed problem with XPFShoppingCartPricing#getTaxes returning the cart total instead of the cart taxes. | 11‑May‑2025 | |
| 92f5a151 | Upgraded certified Oracle version from 19.0.0.0.ru-2024-01.rur-2024-01.r1 to 19.0.0.0.ru-2025-01.rur-2025-01.r2. | Security | 6‑May‑2025 |
| 808f753b | Upgraded certified MySQL RDS version from 8.0.35 to 8.0.41. | Security | 6‑May‑2025 |
| e8f3108f | Fixed vulnerability in DownloadServiceHandler. | Security | 5‑May‑2025 |
| ec1053b1 | Build stability improvements. | 3‑May‑2025 | |
| 2cc22cde | Fixed intermittently failing ExternalPluginTest integration tests. | 2‑May‑2025 | |
| cf8c9bc8 | Upgraded certified MySQL 5.7 Aurora version from 5.7.mysql_aurora.2.11.4 to 5.7.mysql_aurora.2.12.5. | Security | 2‑May‑2025 |
| 1874964c | Fixed intermittently failing "Search product for Merchandising Associations can be filtered by brand" Cucumber test. | 1‑May‑2025 | |
| 87358096 | Added new build plugin that detects when multiple JARs provide the same classes, and outputs this as a warning. | 24‑Apr‑2025 | |
| ae3cb22a | Fixed issue with CouponUsageDaoImpl#findEligibleUsagesByEmailAddressInStore passing wrong value to the named query when email address is empty. | 22‑Apr‑2025 | |
| cd6174e3 | Fixed a performance issue in LocalizedAttributeKeyUtils#getLocaleFromLocalizedKeyName. | Performance | 17‑Apr‑2025 |
| cdd67b7c | Fixed issue with structured error messages from some shopping item validators not showing a link to the affected shopping item. | 11‑Apr‑2025 | |
| fc692311 | Upgraded Tomcat version from 9.0.98 to 9.0.102 to address CVE-2025-24813. | Security | 10‑Apr‑2025 |
| b7e4c7f9 | Allow Cucumber tests in coupon-apply-validation.feature to pass in Trusted Header Mode. | 9‑Apr‑2025 | |
| bea240f5 | Hardcoded "mobee" and "vestri" values removed from scope autocomplete in Cortex Studio. | 4‑Apr‑2025 | |
| e93ab4b5 | Fixed problem with "All Stores" filter being ignored on the customer search tab. | 4‑Apr‑2025 | |
| 2a07d89e | Fixed performance issue when adding actions to catalog promotions in Commerce Manager when database contains a large number of price lists. | Performance | 4‑Apr‑2025 |
| 63b61bb5 | Fixed the Operational Insights revenue calculations to exclude failed and cancelled orders. | 3‑Apr‑2025 | |
| a20620b9 | Improved "View Disabled Data Policy for Customer" Selenium test to not fail on retry. | 3‑Apr‑2025 | |
| 4204486e | Improved performance in Commerce Manager when removing an attribute from a product type. | Performance | 28‑Mar‑2025 |
| 819a3fc1 | Minor code refactoring for TimeIntervalCacheImpl#get to simplify the implementation. | 27‑Mar‑2025 | |
| 40aba2c5 | Fixed search indexing issue in which delete requests are ignored if there are no corresponding add/update requests. | 25‑Mar‑2025 | |
| 02a83ae2 | Fixed issue with structured error messages from some shopping item validators not showing a link to the affected shopping item. | 20‑Mar‑2025 | |
| 4a3a1a25 | Created filter to ensure that the Cortex OSGi console is only accessible on the port specified by ep.management.port. | 14‑Mar‑2025 | |
| b04ff165 | Upgraded netty-handler from 4.1.113.Final to 4.1.118.Final. | Security | 14‑Mar‑2025 |
| 2ce56027 | Removed jakarta-xmlbind Jackson module introduced by Solr 9.8.0 to avoid Jackson module autodiscovery issues. | 12‑Mar‑2025 | |
| 1aa1c732 | Performance optimization for the Extension Point Framework to avoid classpath scanning when extensions are retrieved from the framework. | Performance | 12‑Mar‑2025 |
| 915e2f41 | Allow Cortex to authenticate with JWT tokens when enableTrustedSubjectHeaderMode is enabled. | 12‑Mar‑2025 | |
| 4106b40a | Fixed potential table scan when retrieving the order list in Commerce Manager. | Performance | 10‑Mar‑2025 |
| 79623e18 | Fixed intermittently failing Selenium test "Verify price facets are updated when a promotion is changed". | 7‑Mar‑2025 | |
| ebcdb873 | Initial release of new build tools for configuring a build environment, building and testing the code project, building the set of application container images, and running the application containers locally. | Build Tools | 7‑Mar‑2025 |
| 75212081 | Fixed issue where attributes with keys that match the regex for having a language tag are incorrectly treated as localized attributes when passed to Extension Point Framework entities. | 4‑Mar‑2025 | |
| 248ff5bc | Modified Tax Calculator extension point so that extensions don't need to calculate before tax price for inclusive taxes. | 4‑Mar‑2025 | |
| 331a0967 | Fixed behaviour of the first time buyer flag if the shopper's first order fails. | 3‑Mar‑2025 | |
| 63bf457c | Fixed issue with order hold getting stuck in RESOLVE_PENDING if order lock is present. | 3‑Mar‑2025 | |
| 647ca468 | Fixed issue with Operational Insights interpreting serviceResponseWaitTime in minutes instead of milliseconds. | 28‑Feb‑2025 | |
| 223f7ac2 | Fixed Tax Calculator extension IndexOutOfBoundsException exception for empty tax records collection. | 26‑Feb‑2025 | |
| daaf9bc4 | Fixed issue with Core Request Scoped Caching where some database lookups were not being cached. | Performance | 25‑Feb‑2025 |
| f73122aa | Eliminated unnecessary shopper and shopping cart lookups during cart order retrieval. | Performance | 25‑Feb‑2025 |
| c6c758c9 | Removed unitils-core dependency to address CVE-2016-3093. | Security | 24‑Feb‑2025 |
| a5ce4d69 | Disabled intermittently failing "Verify price facets are updated when a promotion is changed" test. | 22‑Feb‑2025 | |
| 151432e2 | Fixed "bad value for type int" error that appeared in the logs when running Operational Insights with a PostgreSQL database. | 21‑Feb‑2025 | |
| 38d4f0d2 | Ensure that affected products are re-indexed when catalog promotions are added, modified, or become active or inactive to ensure that the indexed price is correct. | 21‑Feb‑2025 | |
| 9e2e1dae | Fixed incorrect environment subfolder names in ext-data. | 18‑Feb‑2025 | |
| e1a37e5d | Removed unnecessary TCUSTOMER index on CREATED_DATE. | Data model changes | 14‑Feb‑2025 |
| db0e540a | Added java.base/java.lang.ref add-open JVM parameter to prevent possible failures when Operational Insights evaluates cache sizes. | 13‑Feb‑2025 | |
| cb7275d0 | Upgraded xstream from version 1.4.20 to 1.4.21 to address CVE-2024-47072. | Security | 13‑Feb‑2025 |
| 7112314b | Enabled HTTP/2 for Solr replication in ops-spec.json. | 13‑Feb‑2025 | |
| d5b06a8d | Removed unnecessary product/category cleanup after Cucumber tests and fixed issue that allowed bundles to be created in Commerce Manager without a valid sku code. | 12‑Feb‑2025 | |
| 3a402df7 | Solr upgraded from 9.4.1 to 9.8.0. | Security | 11‑Feb‑2025 |
| 59e9733f | Fixed race condition that can occur when multiple users execute keyword or navigation searches with different sort keys. | 11‑Feb‑2025 | |
| 7b4f7dc6 | Fixed race condition that can occur when multiple users execute keyword or navigation searches with different sort keys. | 7‑Feb‑2025 | |
| 27d1914b | Fixed intermittent Selenium issue related to case-sensitive ErrorDialog class. | 4‑Feb‑2025 | |
| 173a52af | Build stability improvements. | 30‑Jan‑2025 | |
| 1f131ba0 | Fixed an issue that was causing unnecessary TORDER and TORDERAUDIT update queries to be created. | 28‑Jan‑2025 | |
| cbe22cba | Upgraded Tomcat version from 9.0.97 to 9.0.98 to address CVE-2024-56337 and CVE-2024-50379. | Security | 27‑Jan‑2025 |
| f4f9500a | Fixed issues with the 2024-12-create-missing-indexes changeset caused by needing to modify this changeset in Self-Managed Commerce 8.4 and earlier. | Data model changes | 21‑Jan‑2025 |
| e923786d | Updated getDisplayNames method to lazy loaded in all Extension Point Framework entities to address a potential performance issue when stores have a large number of locales enabled. | Performance | 20‑Jan‑2025 |
| 0e6db98b | Improved performance of Operational Insights revenue query. | Performance Data model changes | 17‑Jan‑2025 |
| fc64bd3f | Fixed incorrect banning of camel-test dependencies. | 17‑Jan‑2025 | |
| b339d89d | Fixed default OpenID Connect identity provider URL in settings files. | 15‑Jan‑2025 | |
| b8aab1ab | Upgraded Camel from 3.14.10 to 3.21.5 to address CVE-2024-22371. | Security | 15‑Jan‑2025 |
| b9b84463 | Removed jetty-runner dependency to address CVE-2024-52046. | Security | 15‑Jan‑2025 |
| 58f10695 | Added missing indexes to PostgreSQL and Oracle that were created implicitly in MySQL. | Performance Data model changes | 14‑Jan‑2025 |
| a91d446b | Updated certified PostgreSQL version from 14.10 to 16.6. | Security | 14‑Jan‑2025 |
| bcd56e2c | Updated Commerce Manager cookies to always set the HttpOnly flag for improved security. | Security | 8‑Jan‑2025 |
| 3e07010c | Changed the orders list on the customer record in Commerce Manager to sort by created date instead of order number to avoid alphanumeric sorting issues. | 7‑Jan‑2025 | |
| aa8d8e69 | Fixed definition of 1FreeForAtleast5AlienSku test promotion. | 7‑Jan‑2025 | |
| e017e07a | Changed coupon validation failure code ERROR_COUPON_USAGE_MISSING to ERROR_EMAIL_NOT_ASSIGNED to improve clarity. | 7‑Jan‑2025 | |
| 0bf048d7 | Added XPFShipmentTypeEnum value SERVICE and deprecated SERVICE_ORDINAL. | 7‑Jan‑2025 | |
| 6786ef68 | Upgraded zookeeper from 3.9.2 to 3.9.3 to address CVE-2024-51504 and CVE-2024-47535. | Security | 6‑Jan‑2025 |
| b4557e57 | Enabled state comparison version strategy on order holds to ensure that two users don't resolve the same hold simultaneously. | 6‑Jan‑2025 | |
| e3777617 | Fixed NullPointerException in ShippingOptionInfoSelectorRepositoryImplTest. | 6‑Jan‑2025 | |
| f53d4a11 | Added system property to ensure that Log4j always uses the BasicContextSelector to avoid OSGi issues in Cortex. | 20‑Dec‑2024 | |
| defd5aee | Changed featuredoffers link on navigations resource from a conditional to a static link to remove unnecessary product query. | Performance | 17‑Dec‑2024 |
| 5af306dc | Added subquery support to JpqlQueryBuilder. | 16‑Dec‑2024 | |
| 9c86b8e9 | Upgraded Spring from 5.3.34 to 5.3.39. | Security | 13‑Dec‑2024 |
| 80058cf0 | Fixed Core Request-Scoped Caching to ensure that retrievals with different load tuners or fetch groups are cached separately. | 10‑Dec‑2024 | |
| 6f79100e | Changed the way that SkuOptionValue is associated with ProductSkuOptionValue, using a lazy load approach instead of the Eager Field Post Load Strategy, to prevent possible "context has been closed" exceptions. | 9‑Dec‑2024 | |
| 6638afd2 | Upgraded Tomcat version from 9.0.85 to 9.0.97. | Security | 9‑Dec‑2024 |
| 481595ed | Removed duplicate and incorrect shopping cart event setting definition bean for determining the shopping cart messaging channel. | 6‑Dec‑2024 | |
| 42e74e19 | Fixed issue where dependent items could not be removed from dynamic bundles in the shopping cart. | 5‑Dec‑2024 | |
| 55e33d5e | Fixed stack trace logging on Camel routes for event-based extension points. | 5‑Dec‑2024 | |
| 4c0dd186 | Upgraded Quartz from version 2.3.2 to 2.4.0 to address CVE-2023-39017. | Security | 4‑Dec‑2024 |
| 00602ab1 | Fixed issue with ProductDaoImpl#findUidBySkuCode that can cause OpenJPA to read all product skus from the database in rare circumstances. | Performance | 3‑Dec‑2024 |
| 10641655 | Fixed intermittent failure in Selenium tests due to problems verifying that a user interface element contains the expected value. | 29‑Nov‑2024 | |
| 019a11be | Fixed intermittent failure in Selenium tests due to problems obtaining focus on a user interface element. | 29‑Nov‑2024 | |
| e45a5180 | Upgraded Jetty from version 10.0.20 to 10.0.24 to address CVE-2024-8184. | Security | 28‑Nov‑2024 |
| 2fdad9f3 | Upgraded Jetty for Wiremock from version 9.4.53 to 9.4.56 to address CVE-2024-22201. | Security | 27‑Nov‑2024 |
| eabf8137 | Upgraded Spring Security from version 5.8.7 to 5.8.14 to address CVE-2024-22257. | Security | 27‑Nov‑2024 |
| 1b149b2d | Upgraded commons-io from version 2.8.0 to 2.14.0 to address CVE-2024-47554. | Security | 26‑Nov‑2024 |
| b3941f9f | Fixed parent references in Commerce Manager modules to improve Maven reactor hygiene. | 26‑Nov‑2024 | |
| 5f63dd86 | Fixed Import/Export to ensure that the necessary product search indexes are rebuilt when base amounts are updated. | 25‑Nov‑2024 | |
| acdaec33 | Updated Wiremock Jetty dependencies from 9.4.49.v20220914 to 9.4.53.v20231009. | Security | 25‑Nov‑2024 |
| 020a55d6 | Fixed intermittent failure in Selenium tests due to problems typing into text boxes. | 25‑Nov‑2024 | |
| 816bba7c | Fixed duplicate dependency definition in the ep-camel-bundle module. | 24‑Nov‑2024 | |
| c6fe30e2 | Removed unnecessary Jetty dependency in webapp-smoketests. | 24‑Nov‑2024 | |
| fdc77a27 | Added a new getAttributeValueByKey method to all Extension Point Framework entities with attributes for use with non-localized attribute values. | 22‑Nov‑2024 | |
| b808e7af | Fixed problem with private use coupon not working for user after added to existing promotion. | 21‑Nov‑2024 | |
| 5eba77d2 | Added jvmRuntimeArguments field to ActiveMQ in ops-spec.json. | 20‑Nov‑2024 | |
| a92f92cd | Improved order hold resolution error handling to ensure that order holds don't get stuck in a pending state. | 19‑Nov‑2024 | |
| 1386d151 | Fixed issue with event-based extension points not supporting multiple extensions on the same extension point. | 19‑Nov‑2024 | |
| e0df5199 | Created ep-camel-bundle bundle so we can avoid embedding Camel dependencies in multiple bundles. | 19‑Nov‑2024 | |
| dab29cb5 | Changed root link expectations in Cucumber tests to prevent failures if new resources are added. | 13‑Nov‑2024 | |
| c16135df | Modified extensions.json requirements so that just the identifier and enabled flag can be specified; all other fields are now optional. | 13‑Nov‑2024 | |
| a095e219 | Renamed notsoldseperately to notsoldseparately in snapitup products.xml. | 12‑Nov‑2024 | |
| aec0b99c | Updated product, product sku, and category default cache timeouts from 1 second to 1 hour. | Performance | 12‑Nov‑2024 |
| 6a8d8c7e | Fixed Cortex structured message response when purchase form is submitted with validation errors. | 12‑Nov‑2024 | |
| d3c5882e | Fixed cart subtotal applied promotions to ensure it only returns the applied 'best of' promotion. | 8‑Nov‑2024 | |
| 57e8551c | Added additional details to the structured error message response when a coupon is determined to be invalid. | 8‑Nov‑2024 | |
| 9948528e | Added new X-Ep-Follow-Location-Status header to indicate the status of the second resource when followLocation is used. | 6‑Nov‑2024 | |
| 8dfae32e | Fixed error handling for shipping option determination so that the actual underlying error is reported rather than a NullPointerException. | 31‑Oct‑2024 | |
| 9443b77a | Fixed a NullPointerException that can occur when publishing multi-sku products through the Data Sync Webapp. | 30‑Oct‑2024 | |
| 49d4271f | Refactored ProductAssociationQueryBuilder to use JPQLQueryBuilder and optimized generated query for determining product associations. | Performance | 29‑Oct‑2024 |
| 084eca93 | Fixed search index rebuild when a product is added or updated using Import/Export. | 29‑Oct‑2024 | |
| fb3332c2 | Upgraded esapi from 2.5.3.1 to 2.5.4.0. | Security | 21‑Oct‑2024 |
| 15e9f9a9 | Upgraded Wiremock from version 2.27.2 to 2.35.1. | Security | 16‑Oct‑2024 |
| 28348a64 | Added pagination support for wish list line items in Cortex. | Performance | 9‑Oct‑2024 |
| 5d0a0102 | Fixed Spring circular dependency that was causing NullPointerExceptions during Integration Server startup. | 8‑Oct‑2024 | |
| 640f0cfb | Fixed preconditions in core-changelog-2020-08-cleanup-expired-failed-orders-job.xml to avoid potential upgrade error. | Data model changes | 3‑Oct‑2024 |
| 5007f8db | Upgraded certified ActiveMQ version from 5.16.7 to 5.18.5. | Security | 26‑Sep‑2024 |
| fb734c0a | Added missing Liquibase checksums to changesets that were updated during the Liquibase upgrade. | Data model changes | 26‑Sep‑2024 |
| ddf3594f | Fixed race condition in TimeIntervalCacheImpl that can result in a NoSuchElementException when retrieving values from the cache. | 26‑Sep‑2024 | |
| f68964b7 | Fixed issue with Cortex attempting to write logs to a folder based on the build machine home folder instead of the runtime machine home folder. | 20‑Sep‑2024 | |
| fcfd8dbc | Removed support for user-name and user-company fields in JWT metadata payload, which was leading to unique constraint errors in PunchOut. | 19‑Sep‑2024 | |
| e5001f89 | Fixed issue with Data Sync Webapp where changesets containing base amounts were causing multiple product index notifications to be created and were also holding the base amount objects in memory until the service was restarted. | 19‑Sep‑2024 | |
| aa055099 | Fixed error that can occur when editing boolean attributes in Commerce Manager. | 14‑Sep‑2024 | |
| 7f98fdd8 | Updated jetty from 9.4.44.v20210927 to 9.4.53.v20231009. | Security | 12‑Sep‑2024 |
| 527cfd95 | Refactored the Catalog Syndication builders to use AbstractBatchJob instead of Spring Batch, to address lock wait timeout issues during the build process. | 11‑Sep‑2024 | |
| ca57f95d | Fixed issues with the shopper conditions user interface in Commerce Manager where conditions were sometimes duplicated or could not be removed. | 11‑Sep‑2024 | |
| bbf48b2b | Ignore lazy loaded Extension Point Framework entity fields when serializing Extension Point Framework entity classes to JSON. | 10‑Sep‑2024 | |
| 66bc2c6b | Colored logging now disabled by default, only enabled for local development deployments. | 2‑Sep‑2024 | |
| 78937a65 | Fix for NullPointerException that can occur if looking up a non-existent compound GUID with CategoryLookup#findByCompoundCategoryAndCatalogCodes. | 30‑Aug‑2024 | |
| 8535dac8 | Fixed NullPointerException in coupon auto-apply role transition if registered user email is null. | 30‑Aug‑2024 | |
| 25ac3f4b | Fix for NullPointerException that can occur if RuleService#findByRuleGuid is called with a non-existent guid. | 28‑Aug‑2024 | |
| ff6e6aa4 | Fixed Commerce Manager error that occurs when searching for products using Advanced Search Query Builder. | 27‑Aug‑2024 | |
| d2410e22 | Updated the Log4j configuration for all services to ensure that log file sizes are limited by using a fixed window rolling policy. | 26‑Aug‑2024 | |
| ee34a55f | Fixed sorting for "Enabled" and "Expiration Date" columns on cart and catalog promotion search results in Commerce Manager. | 26‑Aug‑2024 | |
| 2e5191e6 | Fixed issue where the parentCategoryCodes field is not populated in the SOLR index for linked categories. | 26‑Aug‑2024 | |
| f909f297 | Removed unused CustomerTagStrategy interface. | 21‑Aug‑2024 | |
| 4d58c6ea | Fixed a race condition in service health checks that could report false health check failures if multiple requests are submitted concurrently. | 15‑Aug‑2024 | |
| 204cdb59 | Fixed Catalog Syndication cucumber test stability issue. | 15‑Aug‑2024 | |
| 7b55d07d | Upgraded Tomcat from version 9.0.85 to 9.0.90. | Security | 14‑Aug‑2024 |
| 0a784232 | Fixed issue where the shopping cart memento object was not correctly passed to bundle items during instantiation. | 7‑Aug‑2024 | |
| b0694c2f | Fixed issue with logging of some Catalog Syndication failures. | 6‑Aug‑2024 | |
| 57232e83 | Fixed Cortex keyword search functionality so it correctly reads the COMMERCE/SEARCH/* system configuration settings. | 2‑Aug‑2024 | |
| 9ee21644 | Fixed LibJarUtil parser to properly exclude #runtime refs when scanning the payment plugin classpath. | 2‑Aug‑2024 | |
| 087a922b | Removed checksum validation from core-changelog-2024-07-expired-data-point-values-job changeset due to required changes in earlier versions. | Data model changes | 2‑Aug‑2024 |
| 4607c74b | Improved warning Setting retrieval strategy {} threw an exception to ensure that full stack trace is logged. | 29‑Jul‑2024 | |
| 582e2656 | Fixed SolrFacetAdapter to consistently expect searchCriteria.getSearchHint("priceSourceIds") to contain a list of strings. | 29‑Jul‑2024 | |
| 7725bc2e | Fixed all query strings defined on beans for Catalog Syndication JpaPagingItemReader instances to ensure they have an ORDER BY clause. | 24‑Jul‑2024 | |
| 52ffe73f | Fixed issue where importing entities doesn't properly invalidate the application cache in some circumstances. | 23‑Jul‑2024 | |
| f9f2ba86 | Fixed out of memory error that can occur on the Batch Server if database contains a large number of TCUSTOMERCONSENT records. | 23‑Jul‑2024 | |
| 9e382e7b | Improvements to the Extension Point Framework to support JSON serialization of Extension Point Framework entity objects. | 19‑Jul‑2024 | |
| 3a9e1a72 | Fixed the Commerce Manager status plugin to allow mvn test to work. | 19‑Jul‑2024 | |
| 8dd44edb | Upgraded Apache bval from version 0.4 to 2.0.6. | Security | 17‑Jul‑2024 |
| 8d308c90 | Fixed potential NullPointerException that can occur if opening an address with a null subCountry in Commerce Manager. | 5‑Jul‑2024 |
Badge legend
- Security: Indicates that the patch includes security fixes.
- Performance: Indicates that the patch improves system performance.
- Data model changes: Indicates that the patch includes Liquibase scripts that make changes to the data model.
- Requires downtime: Indicates that the Self-Managed Commerce services should be shut down while the Data Population Tool is executed.
- Build Tools: Indicates that the patch includes changes to Build Tools.
Changelog Announcements
Added build-time checks for multiple JARs providing the same classes
When a Java runtime classpath contains multiple JARs that provide the same fully qualified class name, the classloader will randomly choose one of the class implementations. This can lead to confusing intermittent issues such as MethodNotFound at runtime.
To prevent this, we have added a new plugin to the build process called duplicate-finder-maven-plugin, which detects this situation and logs a warning at build time if it finds multiple JARs providing the same class.
Along with this change, several conflicting dependencies have been resolved:
- Multiple conflicting jars:
jakarta.xml.bind:jakarta.xml.bind-api:2.3.3, javax.xml.bind:jaxb-api:2.3.1javax.xml.bind:jaxb-apiwas removed.jakarta.xml.bind:jakarta.xml.bind-apiis now the primary JAR providingJAXBfunctionality.
- Multiple conflicting jars:
javax.servlet:javax.servlet-api:3.1.0, org.eclipse.jetty.toolchain:jetty-servlet-api:4.0.6org.eclipse.jetty.toolchain:jetty-servlet-apiwas removed.javax.servlet:javax.servlet-apiis now the primary JAR providing servlet functionality.
- Multiple conflicting jars:
org.slf4j:jcl-over-slf4j:1.7.32, org.springframework:spring-jcl:5.3.39, commons-logging:commons-logging:1.1.1commons-logging:commons-loggingwas removed and banned.org.slf4j:jcl-over-slf4jis now the primary JAR providing commons logging functionality.
- Multiple conflicting jars:
aopalliance:aopalliance:1.0, org.glassfish.hk2.external:aopalliance-repackaged:3.1.1, org.springframework:spring-aop:5.3.39aopalliance:aopalliancewas removed and banned.org.glassfish.hk2.external:aopalliance-repackagedis now the primary JAR providingAOPfunctionality.
- Multiple conflicting jars:
jakarta.validation:jakarta.validation-api:2.0.2, javax.validation:validation-api:2.0.1.Final- Core is only using
javax.validation:validation-api(jakarta.validation-apiwas removed). - Search Server is using both:
jakarta.validation-apiversion 3.0.2 which provides thejakarta.validationpackages for SOLR.javax.validation-apiversion 2.0.1 which provides thejavax.validationpackages.
- Core is only using
- Multiple conflicting jars:
javax.el:javax.el-api:3.0.0, org.glassfish:jakarta.el:3.0.4jakarta.el:jakarta.el-apiandjavax.el:javax.el-apiwere removed and banned.org.glassfish:jakarta.elis now the only JAR providing expression language functionality.
- Multiple conflicting jars:
io.swagger.core.v3:swagger-annotations-jakarta:2.2.22, io.swagger.core.v3:swagger-annotations:2.1.13io.swagger.core.v3:swagger-annotationswas removed and banned.io.swagger.core.v3:swagger-annotations-jakartais now the only JAR providing Swagger annotations functionality.
- Multiple conflicting jars:
com.sun.mail:imap:1.5.6, com.sun.mail:jakarta.mail:1.6.7, com.sun.mail:javax.mail:1.5.6com.sun.mail:javax.mail,com.sun.mail:imap,javax.mail:mailapi, andjavax.mail:mailand were removed and banned.com.sun.mail:jakarta.mailis now the only JAR providing mail functionality.
- Multiple conflicting jars:
com.sun.activation:jakarta.activation:1.2.2, com.sun.activation:javax.activation:1.2.0, jakarta.activation:jakarta.activation-api:1.2.2, javax.activation:activation:1.1com.sun.activation:javax.activation,javax.activation:activation,javax.activation:javax.activation-api, andjakarta.activation:jakarta.activation-apiwere removed and banned.com.sun.activation:jakarta.activationis now the only JAR providing activation functionality.
If you encounter a banned dependency error after consuming these patches, follow these steps to address the error:
- In your terminal, navigate to the module where the banned dependency was found. (i.e.
cd extensions/integration/ext-integration-webapp) - Run
mvn dependency:treeto view the dependency tree and determine where the banned dependency is coming from. - If the banned dependency is a direct dependency, you should remove it from the POM file.
- If the banned dependency is a transitive dependency, add an exclusion to the dependency that is including the banned dependency.
- Run
mvn dependency:treeagain to verify that the banned dependency is no longer in the dependency tree.
Solr upgraded from 9.4.1 to 9.8.0
This upgrade resolves several CVEs:
- CVE-2024-45216 (CVSS3 score 9.8) raised on 2024-10-16.
- CVE-2024-45217 (CVSS3 score 5.3) raised on 2024-10-16.
- CVE-2025-24814 (CVSS3 score 9.1) raised on 2025-01-27.
- CVE-2024-52012 (CVSS3 score 7.6) raised on 2025-01-27.
However, this upgrade also causes Solr to use HTTP/2 by default for index replication between the leader (primary) and replica (follower) nodes. As a result, Solr replication will fail unless at least one of the following actions is taken:
- Enable HTTP/2 support in the Tomcat server used by the Solr leader. Upgrading to Elastic Path Docker version 4.5.6, 4.4.7, or 4.3.7 will do this automatically.
- Set the following JVM parameter on the Solr follower Tomcat instance:
-Dsolr.http1=true.
8.6.0
Released: June 2024
Release highlights
OpenID Connect integration for business users
Commerce Manager now has the ability to authenticate business users using a third-party Identity Provider. If enabled, business users will have the option to sign in as a local user with their existing username and password (if present), or login using the enterprise Identity Provider. Use of a third-party Identity Provider can improve security and allow single-sign-on across multiple web applications.
For more information, see Commerce Manager Enterprise User Authentication.
Split payments
This feature allows shoppers to pay for their shopping cart purchase by splitting the total across multiple payment instruments. Payment can be split across any supported payment methods, including different credit cards, gift cards, direct debits, or any other payment method provided by a payment plugin.
To support this, the Cortex API now allows multiple payment instruments to be selected on the cart order. Exactly one of the payment instruments must have a limit of 0, which means "unlimited". All other payment instruments must have a limit set. When checkout occurs, the payment system will charge the limit amount on each payment instruments with limits, and charge the remainder of the order total on the unlimited payment instrument. In case of failure during the reserve phase of any payment instrument, any payment instruments that have already been reserved will have their reservations cancelled automatically.
For more information, see Checkout Payment Instruments.
Shopping Cart Line Item promotions
Shopping cart promotions can now be configured to either evaluate conditions and actions at the cart level (matching the behaviour in all previous versions of Self-Managed Commerce), or at the cart item level.
If Define cart level rules is selected, then the promotion conditions will be evaluated on the entire cart, and the actions will apply to the entire cart if the conditions are satisfied.
If Define line item level rules is selected, then the promotion conditions will be evaluated on each individual cart line item, and the actions will apply to the line item if the conditions are satisfied.
This new feature allows your merchandiser to define discounts that are activated by very specific conditions related to a particular shopping cart line item.
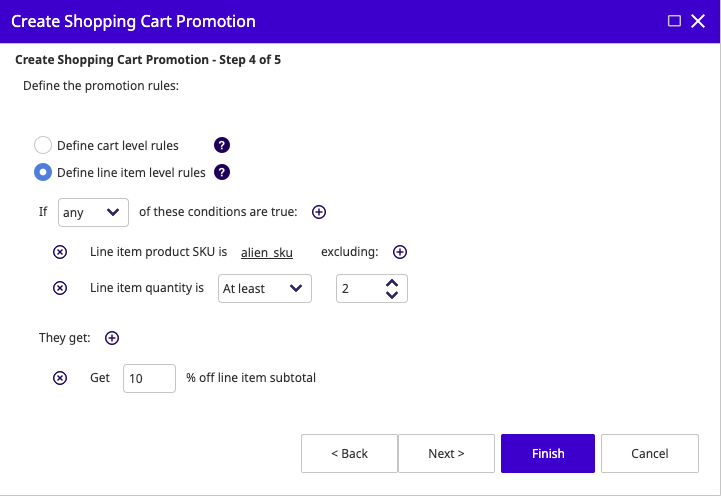
For more information, see Creating a Shopping Cart Promotion.
Ability to filter promotions based on selling context fields
Merchandisers can now search for catalog and shopping cart promotions that would apply to a simulated shopper with particular attributes. For example, if a simulated shopper is configured with age 18, then any promotion with shopper conditions that require that the shopper be that age will be returned.
Merchandisers can also search for promotions that apply to all shoppers (i.e. no shopper conditions) or that apply on a specific date and time (i.e. a date that falls between the promotion start date and end date).
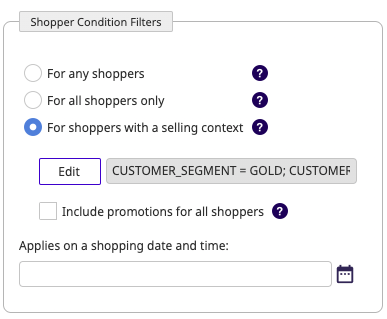
For more information, see Searching for a Catalog Promotion and Searching for a Shopping Cart Promotion.
Promotion carrots for catalog items
On a product display page, your merchandisers may want to entice shoppers with the promotions that are potentially available if they add the product to cart. For example, if the shopper is looking at a iPhone 14 product page, we want to show them that a buy-one-get-one offer or a free item is available once they add the product to cart. There might also be other conditions that need to be satisfied, such as a certain quantity, or another item in cart, etc.
Promotion carrots addresses these use cases by exposing a new link on the item resource called promotioncarrots. This new resource shows a list of elements that represent shopping cart promotions that are related to the item (product SKU). For example, if all of the promotion shopper conditions apply, and the promotion has a condition that the item's product SKU must be present in the cart, it will be included in the results.
The front-end can either use the carrot description specified by the business on each promotion, or can use the detailed condition and action details from the response to generate a description that is meaningful to the shopper.
For more information, see Read Promotion Carrots for an Item.
Shopping Cart Events extension point
A new extension point has been added that notifies extensions when shopping cart events occur. This allows Extension Point Framework extensions to make decisions based on shopping cart events or inform back-end systems about shopping cart changes.
For more information, see Shopping Cart Events extension point.
Shopping Cart Line Item Events extension point
A new extension point has been added that notifies extensions when shopping cart line item events occur. This allows Extension Point Framework extensions to make decisions based on shopping cart line-item events or inform back-end systems when items are added or removed from cart.
For more information, see Shopping Cart Item Events extension point.
Customer Events extension point
A new extension point has been added that notifies extensions when customer events occur. This allows Extension Point Framework extensions to make decisions based on customer events or inform back-end systems when customers register, authenticate, or make profile changes.
For more information, see Customer Events extension point.
Order Release Events extension point
A new extension point has been added that notifies extensions when a purchase is confirmed and ready to be sent to the fulfillment system. This allows Extension Point Framework extensions to inform back-end systems when a purchase is ready to be fulfilled.
For more information, see Order Release Events extension point.
Message-based cache invalidation for products
When products are updated, either through Commerce Manager, Import/Export, or Data Sync Webapp, these changes are now reflected immediately in Cortex API responses. Since products are cached in Cortex, these changes would previously take up to an hour to be reflected in API responses.
Now when products are updated, a domain event is processed by Integration Server, which triggers a topic broadcast to all services in the environment. Then this broadcast is received, the services evict the product from their local Ehcache.
Message-based cache invalidation for other entities such as base amounts (prices) and promotions will be added in future Self-Managed Commerce versions.
For more information, see Application Caching using Ehcache.
Support for street line 3 on addresses
Support for a third street line has been added to all addresses. This includes the following changes:
- All Commerce Manager address forms now show an "Address Line 3" field.
- All address objects in Import/Export now support a
street3field. - All Cortex address forms now have
street-address,street-address-2, andstreet-address-3fields. Theextended-addressfield is deprecated. If a client posts a form with this field, it will map to thestreet-address-2field for backwards compatibility. The response will includestreet-address,street-address-2,street-address-3, andextended-addressfields, butstreet-address-2andextended-addresswill contain the same values. - The customer address CSV import now supports a
street3field. - Data policies now support the
STREET_3field. - All standard email templates with addresses will now display street address line 3.
New in this release
In addition to the Release Highlights, this release contains the following updates:
Customer Data Tag Set Populator extension point
A new extension point has been added that allows an extension to access customer and account records and use those details to add fields to the tag set. Those fields can then be used in promotion and price list assignment conditions.
For more information, see Customer Data Populator extension point.
Added "Never available" option to product availability rules
Added a new option to product availability rules called "Never available". This will ensure that the product will always appear as out-of-stock.
The complete list of product availability rules is as follows:
- Available only if in stock
- Available on pre order
- Available on back order
- Always available
- Never available
These availability rules will only apply to skus that are configured as "Shippable". "Digital Asset" skus are treated as "Always available" regardless of the product available rule setting.
Added ability for buyers to determine their role in each account they're associated to
For buyers who are associated to accounts, they can see all the accounts they are associated to by reading defaultprofile --> accounts --> element. Within each account, buyers can also see all associates by accessing associates -> element. Within this associate resource, the user's role, email, first name, and last name is visible.
However, this made it difficult for the logged-in buyer to determine their own role in each account. To address this, the associates resource now returns an activeuser link, which returns the associate details for the currently logged-in buyer.
Added pagination support for shopping cart line items and purchase line items in Cortex
Added a new link to the carts.cart and purchases.purchase resources named lineitemspaginated. This returns the same elements as the existing lineitems link, but the results are paginated. The page size is defined by the COMMERCE/STORE/listPagination setting value. An example response from the lineitemspaginated resource is shown below:
{
    "self": {
        "type": "carts.paginated-line-items",
        "uri": "/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitemspaginated/1",
        "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitemspaginated/1"
    },
    "messages": [],
    "links": [
        {
            "rel": "element",
            "type": "carts.line-item",
            "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitems/hfrdaolghazdmljrmq2tcljumntdmllbgvrdallege2gioldmu4deojqgu="
        },
        {
            "rel": "element",
            "type": "carts.line-item",
            "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitems/gqydezrymnrteljtgrrdcljumm2dellbheygcljvmi3ggzjyhe2wknlfmy="
        },
        {
            "rel": "element",
            "type": "carts.line-item",
            "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitems/ga3dizjqg43tcljugizwmljugbsdcllbmezdqllemiztazrtgeztenzxgi="
        },
        {
            "rel": "element",
            "type": "carts.line-item",
            "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitems/g4ytqzbsmfsdsllbmrqwiljuhaydcljzguzwcllcgyztiojsgfqwiylbmm="
        },
        {
            "rel": "element",
            "type": "carts.line-item",
            "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitems/giztsojwgzrwkllbgmztmljug42teljyg4zwkljsmiztanjwmjrtiy3emi="
        },
        {
            "rel": "next",
            "type": "carts.paginated-line-items",
            "href": "http://epc-sandbox.elasticpath.net:8080/cortex/carts/mobee/he3tmobuha3teljwmi2tiljuhfrdgllcgfqwelldmy2tozrqmeytmnzrha=/lineitemspaginated/2"
        }
    ],
    "pagination": {
        "current": 1,
        "page-size": 5,
        "pages": 2,
        "results": 7,
        "results-on-page": 5
    }
}
Soft delete shopping carts
When user deletes a custom shopping cart through Cortex, the cart is no longer deleted immediately. Instead, the status is set to INACTIVE, the same behaviour that occurs when checking out a shopping cart.
The InactiveCartsCleanupJob will then delete all inactive shopping carts asynchronously. However, a new setting has also been added to this job named COMMERCE/SYSTEM/INACTIVECARTSCLEANUPJOB/minAge, which controls the minimum number of minutes after last modification for an inactive shopping cart to be cleaned up. This delay was added to ensure that the Shopping Cart Events extension point has the opportunity to retrieve details about a deleted cart before the record is deleted from the database.
Gift Certificate payment plugin
For many years, Self-Managed Commerce has supported the ability for shoppers to purchase a product that generates a gift certificate balance that is tracked in the application. However, the only way to allow that gift certificate balance to be used by shoppers required consuming the Pay with Gift Certificates Accelerator.
Now, Self-Managed Commerce 8.6 provides a built-in payment plugin for making purchases using the gift certificate balance. In combination with Split Payments, this allows shoppers to pay for purchases with a combination of gift certificate balance and another payment method.
This functionality completely replaces and deprecates the Pay with Gift Certificates Accelerator.
For more information, see Payment Plugins.
The Operational Insights API now reports JVM timezone configuration
In the Operational Insights API response, the configuration --> ep-services --> [SERVICE_GUID] --> jvm node now contains a field called jvm-timezone, which reports the timezone offset as determined by the JVM. This allows the Operational Insights front-end to report a severe error if the database timezone and the applications server timezone do not match, which can lead to timezone conversion issues.
Added ability to copy a coupon code to the clipboard from Commerce Manager
When viewing a coupon code in the coupon code editor in Commerce Manager, the field is now in a read-only text box so users can highlight the code and copy it to their clipboard.
Performance Insights HTML report now includes a link to a CSV file showing JPQL query count differences
When viewing the HTML report for a Cucumber test run that compares against the release baseline, there's a new column named "Query Diffs" that contains a link. This link resolves to a CSV file that shows a list of all JPQL queries that either increased or decreased in count. The first column of the report is the JPQL query, and the second column is how much the count increased (positive value) or decreased (negative value).
For more information, see Performance Insights Reports.
Support for interleaving of version-specific platform Liquibase changesets and custom Liquibase changesets
Until now, to make schema changes in the database through Liquibase changesets, Self-Managed Commerce only supported a single injection point for custom Liquibase changesets: The extensions/database/ext-data/src/main/resources/schema/schema-customizations-changelog.xml Liquibase changelog file.
The Liquibase changesets in this file are always executed after all other schema modification changesets by Data Population. This can create a problem if a patch or version upgrade provided by Elastic Path modifies a table or index that a custom changeset is accessing or modifying.
As an example, assume that your company is using Self-Managed Commerce 8.5, and you create a custom Liquibase changeset to add a column to the TSHOPPINGITEMRECURRINGPRICE table. This changeset is part of the extensions/database/ext-data/src/main/resources/schema/schema-customizations-changelog.xml Liquibase changelog file, so it's evaluated last. Later, when upgrading to Self-Managed Commerce 8.6, that table is removed by a platform Liquibase changeset. When updating an existing database, everything appears to work as expected because Liquibase detects that the changeset to add the column to TSHOPPINGITEMRECURRINGPRICE was already executed and skips it. However, if a database is reset, the platform changeset to drop the table is executed first, and then the custom changeset to add the column is executed, but fails because the table no longer exists.
To address these issues, the extensions/database/ext-data/src/main/resources/schema folder now contains Liquibase changelog files for each version. Self-Managed Commerce 8.6 supports the following changelog files:
schema-customizations-changelog-820.xml: Executed after all release changesets for Self-Managed Commerce 8.2 and earlier, but before any 8.2 patch changesets or 8.3 release changesets.schema-customizations-changelog-830.xml: Executed after all release changesets for Self-Managed Commerce 8.3, but before any 8.3 patch changesets or 8.4 release changesets.schema-customizations-changelog-840.xml: Executed after all release changesets for Self-Managed Commerce 8.4, but before any 8.4 patch changesets or 8.5 release changesets.schema-customizations-changelog-850.xml: Executed after all release changesets for Self-Managed Commerce 8.5, but before any 8.5 patch changesets or 8.6 release changesets.schema-customizations-changelog-860.xml: Executed after all release changesets for Self-Managed Commerce 8.6, but before any 8.6 patch changesets or 8.7 release changesets.schema-customizations-changelog.xml: Executed after all release changesets. This file continues to be supported for backward compatibility but is no longer recommended for use.
If the Liquibase changeset to add the column to TSHOPPINGITEMRECURRINGPRICE is moved to schema-customizations-changelog-850.xml instead of schema-customizations-changelog.xml, it will always be executed before the platform changeset for Self-Managed Commerce 8.6 that dropped this table, and no failure occurs.
Messages in ActiveMQ are now discarded automatically if not retrieved after a week
If messages are delivered to ActiveMQ queues that do not have consumers, then messages will accumulate until the storage limit of KahaDB is reached, or the machine runs out of disk space.
To address this, all messages sent to ActiveMQ now have a time-to-live defined. This value is set to one week (604800000 ms) by default, but can be overridden by setting the -Dep.jms.ttl JVM parameter. Additionally, the ActiveMQ configuration has been modified to ensure that expired messages are discarded rather than being moved to a dead letter queue.
Messages in a dead letter queue due to repeat failed processing attempts will not be discarded.
Fixed issues
Commerce Manager
Changed boolean attribute value dialogs to use consistent terminology
All boolean attribute values displayed in Commerce Manager now use true/false terminology instead of yes/no and true/false inconsistently.
Cleaned up warnings in Commerce Manager startup log
Fixed an issue that was causing warnings to appear in the Commerce Manager logs during startup. The warnings looked like the following:
cm              | !ENTRY org.eclipse.rap.ui 2 0 2024-03-19 14:28:26.394
cm              | !MESSAGE Warnings while parsing the images from the 'org.eclipse.ui.commandImages' extension point.
cm              | !SUBENTRY 1 org.eclipse.rap.ui 2 0 2024-03-19 14:28:26.394
cm              | !MESSAGE com.elasticpath.cmclient.core.commands.ChangePassword: plug-in='com.elasticpath.cmclient.core'
cm              | !SUBENTRY 1 org.eclipse.rap.ui 2 0 2024-03-19 14:28:26.394
cm              | !MESSAGE com.elasticpath.cmclient.core.commands.ChangePagination: plug-in='com.elasticpath.cmclient.core'
cm              | !SUBENTRY 1 org.eclipse.rap.ui 2 0 2024-03-19 14:28:26.394
cm              | !MESSAGE com.elasticpath.cmclient.core.commands.AboutApplication: plug-in='com.elasticpath.cmclient.core'
cm              | !SUBENTRY 1 org.eclipse.rap.ui 2 0 2024-03-19 14:28:26.394
cm              | !MESSAGE com.elasticpath.cmclient.core.commands.ChangeTimezone: plug-in='com.elasticpath.cmclient.core'
cm              | !SUBENTRY 1 org.eclipse.rap.ui 2 0 2024-03-19 14:28:26.394
cm              | !MESSAGE com.elasticpath.cmclient.core.commands.Docs: plug-in='com.elasticpath.cmclient.core'
Cortex
Orders are now placed on hold if a payment plugin sets requestHold field
Since version 8.0, the PaymentCapabilityResponse object that is returned by payment plugins has had a requestHold field. However, the platform has been ignoring this value. Now, if a payment plugin sets this field as part of the reserve method implementation, Self-Managed Commerce will place a hold on the order.
Example payment plugin implementation:
@Override
	public PaymentCapabilityResponse reserve(final ReserveCapabilityRequest reserveCapabilityRequest) throws PaymentCapabilityRequestFailedException {
		// Create pre-authorization through payment gateway APIs

		PaymentCapabilityResponse paymentCapabilityResponse = new PaymentCapabilityResponse();
		paymentCapabilityResponse.setData(paymentCapabilityResponseData);
		paymentCapabilityResponse.setProcessedDateTime(LocalDateTime.ofInstant(Instant.ofEpochSecond(paymentIntent.getCreated()), ZoneOffset.UTC));
		paymentCapabilityResponse.setRequestHold(true);

		return paymentCapabilityResponse;
	}
Re-exposed Apache Camel JMX MBeans
After upgrading Apache Camel from 2.25 to 3.14, the Apache Camel JMX MBeans were no longer exposed. Now these MBeans are available for all services except Cortex.
Updating a cart line item no longer deletes and recreates the cart line item database record
Previously, updating the quantity of a cart line item or the modifiers on a cart line item would actually result in delete and insert database operations. This was very inefficient, and resulted in a lot of unnecessarily complex code to deal with child line items. This has been simplified so now a simple update database operation is performed.
Refactored how shopping cart line items are loaded from the database
Shopping cart line items are complex entities because they can have multiple levels of children. To avoid making queries for all of the children of every line item at each level of the tree, a method called ShoppingCartServiceImpl#restoreDependents would retrieve all cart line items in a single query and allocate them to the correct root line items. However, this confused OpenJPA and resulted in problems when trying to update the shopping cart line items later.
To resolve this, we changed the ShoppingCartImpl domain class so that it loads all shopping cart line items (regardless of position in the tree) into a single collection. We then removed the list of child items from each shopping item and instead created methods that retrieve the child items on demand by retrieving them from the list based on their parent line item GUID.
This change greatly simplified the JPA object graph and allowed us to remove some complex logic that was causing problems.
Payment failures during checkout should not include stack trace in structured error response
Fixed an issue where a complete stack trace was being included in a field of the structured error message called InternalMessage when an error occurred during payment processing. This field has been replaced with a field called cause that includes a simple text message that explains the reason for the failure. Example:
{
  "messages": [
    {
      "type": "error",
      "id": "payment.failed",
      "debug-message": "Error occurred when processing payment.",
      "data": {
        "cause": "Not enough balance on this gift certificate."
      }
    }
  ]
}
Fixed issue with Cortex refusing to load promotion rules if they didn't exist on first attempt to load them
Due to a caching bug, if Cortex attempted to load compiled rules from the TRULESTORAGE table before Search Server finished building them, the Cortex server would never attempt to load them again. This resulted in promotions not being calculated until the server was restarted. Now, the cache is aware of the compiled rules are not present and will periodically check the database to see if the rules are available.
Made several improvements to api-platform exception handling
Fixed several issues related to how exceptions are handled in Cortex resources:
-
When an unexpected exception is reported in the Cortex response body for a resource, the reference number in the response now matches the logged reference number. Example:
Server failure processing resource operation. See log for details. Ref#214ce0f1-8268-11ee-bea8-a2b04d2007df -
When an unexpected exception is reported in the Cortex response body for an advisor, the response now includes a reference number that matches the logged reference number. Example:
"messages": [{"type": "error","id": "advisor.internal.error","debug-message": "Server failure processing advise operation. Ref#a17954ce-8272-11ee-8b25-a2b04d2007df","blocks": {}}] -
The full stack trace was not being logged in some circumstances.
Added the Vary header to Cortex responses to prevent client-side caching issues
Front-ends using Javascript to access Cortex were finding that the browser was only using the request URI as the key for browser caching. This caused several issues, for example:
- If a user logs out and a new user logs in, the new user might see the old user’s responses.
- If the selected account is changed, the user might see responses from a different account, or from when no account was selected.
- If the language is changed, the user might see responses from the old language.
The reason for this is that Cortex returns header Cache-Control: private with many responses. This means that the browser is permitted to cache the response for the current machine. However, since Cortex was not also sending the Vary header, only the request URI was used in the cache key.
The HTTP Vary header allows a service to tell upstream caches (such as browser caches) that the response body is influenced by the value of certain request headers. By default, Cortex now sends this header with all responses:
Vary: authorization, accept, accept-language, x-ep-account-shared-id, x-ep-user-traits, x-ep-user-id, x-ep-user-roles, x-ep-user-scopes, x-ep-data-policy-segments
The values returned by this header can be overridden by setting the cortex.response.header.vary JVM parameter.
Cortex Studio
Added option to control whether or not browser caching should be used
By default, all HTTP requests from Studio to Cortex include a cache busting query parameter like this: ?_=1694273409740. This ensures that the browser will always make a request to Cortex rather than using the browser cache to return the response. In some cases, it may be necessary to disable the cache busting parameter, such as when testing client-side caching of Cortex responses. Therefore, a new checkbox has been added to the "Setup" section of studio named "Bypass Browser Caching". When enabled (which is the default), the cache busting query parameter will be added to ensure that the client-side cache is not used. When disabled, the cache busting query parameter will not be used, and duplicate requests may come from the client-side cache.
Integration Server
Orders with a physical shipment are no longer released until the shipment is released
Previously, when an order was first created, the InitiateFulfilmentCheckoutAction checkout action executed by the Integration Server (as part of the PostCaptureCheckoutService) would call OrderService#releaseOrder right away. This "release order" method does a few things including changing the order status to IN_PROGRESS and sending the ORDER_RELEASED event. The ORDER_RELEASED event tells listeners that it is safe to release the order to fulfillment (i.e. ship the product to the customer). In Self-Managed Commerce 8.6, this event tells Integration Server to trigger all extensions assigned to the Order Release Events extension point.
The issue with this behavior was that the physical shipment could still be in the INVENTORY_ASSIGNED state, meaning that business users are still permitted to modify the shipment before it goes to fulfillment. There is a "pick delay" configuration on the warehouse that defines how long physical shipments should stay in this state before they are released. Alternatively, business users can manually release physical shipments through Commerce Manager.
The new behaviour ensures that orders with a physical shipment are only released by the InitiateFulfilmentCheckoutAction checkout action once the physical shipment is released. This ensures that the order is only released to fulfillment after the shipment can no longer be modified by business users.
The Catalog Syndication history table has been dropped
Previously, when Catalog Syndication projections were built by Batch Server, if a previous snapshot of an entity existed, it was copied from the TCATALOGPROJECTIONS table to the TCATALOGHISTORY table. However, no APIs were provided for accessing the data in this table, and the table often grew to an extremely large size with no real benefit.
Therefore the TCATALOGHISTORY table has now been removed, and the Catalog Syndication projection builder no longer populates these records. The cleanupCatalogSyndicationHistoryJob Batch job has also been removed.
The Integration Server readiness health check no longer validates that Search Server indexes are fully built
Previously, the Integration Server readiness health check would fail until the related Search Server completed. This was causing several issues:
- The deprecated health check endpoints were delegating to the readiness checks (not the liveness checks) so they were taking much longer to pass, resulting in services being restarted while the search indexes were being built.
- The smoke tests were expecting Integration Server readiness checks to fail, because they weren't waiting long enough for the search indexes to complete building.
- An Integration Server often connects to several load-balanced Search Servers, which can each be at different states of index completion, which can result in strange results from the Integration Server health checks.
As a result of these issues, we removed this step from the Integration Server readiness health check.
Fixed issue with Operational Insights sometimes returning partial responses
Previously, when an Operational Insights API request was received, Integration Server would wait for a fixed period of time for all responses to arrive from running services. This meant that sometimes it would delay unnecessarily, and sometimes it would not wait long enough for all responses to arrive.
Now, Operational Insights first sends out a "ping" request to all services to determine what is running in the environment. Then it requests the configuration and runtime details and waits until replies are received from all running services before returning the consolidated response. This ensures that all services are given enough time to generate a reply which can be included in the response.
Search Server
Invalid compiled Drools rules are now automatically deleted
A startup check was added to the Search Server to determine if the rules compiled into the TRULESTORAGE table are invalid. This usually occurs if the Drools version was upgraded which results in errors occurring when the compiled rules are retrieved. Once the rules are deleted, Search Server will rebuild the contents of the TRULESTORAGE table automatically.
Fixed issue with Search Server freezing during shut down if index build was in progress
If a user attempted to terminate Search Server while an index build was in progress, the service would lockup and would need to be forcibly killed. This has now been resolved.
Batch Server
Changed the behaviour of the batch size configuration parameter for data cleanup jobs
Each data cleanup job in the Batch Server is configured with a batchSize parameter (i.e. COMMERCE/SYSTEM/ANONYMOUSCUSTOMERCLEANUP/batchSize). Previously, this value simply indicated how many records would be processed in a single transaction, and the cleanup job would always keep executing batches until all available records were processed. Now, the cleanup job will only process up to the number of records specified by batchSize (in a single transaction) and then stop. Any remaining records will be processed in the next scheduled execution of the job.
Improved Catalog Syndication cleanup process to run in batches to avoid lock wait timeouts
When the Catalog Syndication projection build is run with the cleanUpDatabase option set, the cleanup operation now runs in a batch operation so that large deletes do not timeout.
Import/Export
Improved Import/Export exception stack trace
In some circumstances, if a problem was detected in the data being imported, Import/Export would throw an exception that was logged as follows:
com.elasticpath.importexport.common.exception.runtime.PopulationRollbackException: null
This exception didn't provide any details about the nature of the issue that was found. This has been improved, so the exception now shows the details of the problem.
Fixed issue with unexpected locales being included when exporting locale-specific attribute values
When exporting attribute values with locale-specific values, unexpected locales were being included in the results. This was due to Import/Export generating values for all locales supported by the JVM. Now, only locale-specific values present in the databse will be exported.
Exporting data using Maven no longer requires ep.debug.port to be specified
When exporting Import/Export data using Maven, the Maven command would fail unless the ep.debug.port property was specified. Now it defaults to 8000 so it can be run without specifying this property.
Added additional validation to order import functionality
Added additional validation to Import/Export for orders to ensure that child records aren't accidentally transferred from one order to another by importing a child record with a GUID that already exists in the database. Affected child record types include order skus, shipments, payments, and order payment instruments.
Database
Multiple improvements to PostgreSQL support
In PostgreSQL, a server can contain multiple databases, and each database can have multiple schemas. Previously, we allowed the database to be selected by setting the epdb.databasename JVM parameter, but Self-Managed Commerce would always use the public schema. Now, the schema can also be selected by setting the epdb.schemaname JVM parameter.
Additionally, when running reset-db on PostgreSQL, the initialization script would drop and recreate the user, which would also drop all objects owned by that user, including schemas. In Self-Managed Commerce 8.6, the user is only created if it doesn't already exist, and users are never dropped.
Finally, the uuid-ossp extension is now installed in the pg_catalog schema, allowing it to be used by multiple schemas. This allows the creation of multiple Self-Managed Commerce schemas on a single PostgreSQL database.
Moved wish list items out of TCARTITEM table into new TWISHLISTITEM table
Previously, both shopping cart line items and wish list items were stored in the TCARTITEM table. To support this, TCARTITEM contained nullable SHOPPINGCART_UID and WISHLIST_UID fields. Due to this architecture, there was a chance for table scans to occur when filtering on these fields due to low cardinality of the indexed field.
To address this, a new TWISHLISTITEM table has been created and all wish list items have been moved into this table. Additionally, the SHOPPINGCART_UID field has been changed to non-nullable, and the WISHLIST_UID field has been removed from TCARTITEM.
Additional Commerce Engine fixes
- When extensions implementing
ProductSkuValidatorwere being called, theXPFProductSkuValidationContext#getParentProductSkumethod was always returning null during cart update operations, even if the cart line item had a parent line item. - The custom
RandomGuidImplclass for generating UUIDs has been removed and all uses of this class have been refactored to use the Java-providedUUID#randomUUIDmethod instead. The custom class was using the MD5 hash, which was being flagged as having a "weak pseudo-random" vulnerability. - Fixed some small inconsistencies between services regarding where the
ep.propertiesandep.override.propertiesfiles were expected to be found. Those inconsistencies have been resolved and all services now look for these files in the locations documented in Spring Configuration. - Updated all Camel routes to extend
CRSCEnabledRouteBuilderso they properly evict the Core Request-Scoped Cache and avoid dirty reads. - Fixed an issue where a caching logic bug caused the
TimeService#getTimeZonemethod to intermittently return null. - When publishing change sets, email notifications indicating success or failure were not being delivered to the change set owner. This has now been resolved.
- Removed confusing optional
contextsparameter fromSettingsReader#getSettingValueswhich didn't work as expected and was unused. - Fixed issue where
CouponUsageLimitValidatordidn't properly handle some coupon-related issues. - Fixed an issue where the post capture checkout process was unintentionally retried multiple times if there was an exception thrown.
- Fixed a potential race condition around initialization of the
CategoryLookupandCategoryServiceload tuners which could cause errors about unloaded fields. - Fixed issue where the Cortex health checks may read the internal health check URL using the wrong Tomcat connector, which can cause the health checks to show Cortex as healthy before startup completes.
- Added an exclusion on Spring Framework dependencies within
ext-commerce-engine-wrapperto ensure that Spring dependencies aren't accidentally embedded in the bundle. This implements the suggested recommended in this Expert Blog post. - The
ep-rest-repositories-epcommercemodule was previously defined as a bundle, but was not deployed as a bundle. This module has been renamed toep-cortex-repositoriesand is now embedded within theext-cortex-repositoriesbundle. Themaven-bundle-pluginplugin has been removed, and thepom.xmlfile now defines this module as a jar. - Due to an issue in the
permission.propertiesconfiguration in thecart-->lineitems-->element-->dependentoptionsresource, an "Authorization failed" error was appearing in the Cortex logs. This has now been resolved. - Removed the logic that allowed cached tax calculation for a shopping cart to be reused when checking out, which was unnecessarily complex and was causing a possible issue where tax calculation failures could occur.
- Fixed an issue where the
storewas not always set properly on theXPFProductSkuobject when a shopping item context was created. - Removed code that could change a customer's associated store code when they log into a linked store.
- Fixed issue for scenario when multiple customer records have the same username for different stores, the wrong customer record could be selected during authentication.
- Fixed a
NullPointerExceptionthat can occur if custom code attempts to save a sku option value usingSkuOptionService#add(SkuOptionValue). - Changed the "Less shipment discount" label on the Commerce Manager shipment summary to always appear as black.
- Added
java.base/java.lang.invoketoadd-opensto resolve a potential Helix Validator plugin failure. - Added additional
add-opensJVM parameters to prevent possible failures when Operational Insights evaluates cache sizes. - Fixed exception handling when an unexpected attribute value type was read from an attribute value table.
- Improved exception handing around customer creation logic to ensure that root cause is properly logged.
- Fixed anonymous customer cleanup job failure that occurs if a customer has wish list items.
- Fixed issue with the ActiveMQ console showing an error when accessed on a local developer machine.
- Fixed issue where a selling context condition that uses "not matching" or "not containing" incorrectly evaluated to false if the key was not present in the tagset.
- If order hold resolution fails due to a locked order, process will now retry automatically.
- Fixed race condition that can occur if a user posts multiple requests to the registration form concurrently. This change ensures that only a single authentication record is created in this circumstance.
- Fixed Cortex permission error that can occur if
x-ep-account-shared-idheader is set when reading accounts associated to the current user. - Fixed Cortex server error that occurs when reading applied promotions on a shopping cart where one or more line items has no price.
- Fixed a failure in the
wishlistmembershipresource if a wish list contains the same product sku more than once. - Fixed a
NullPointerExceptionthat can occur if looking up a non-existent category GUID withCategoryLookup#findByGuid. - Modified the handling of email localized property values so that properties that are explicitly set to empty string result in an empty string being used as the value.
- Fixed usages of
COMMERCE/SYSTEM/FILTEREDNAVIGATION/separatorInTokenso the setting works as expected. - Fixed issue with Query Analyzer associating SQL queries to the wrong JPQL query in some circumstances.
- Fixed issue where physical product inventory was not properly released if an order failed.
- Fixed issue with offer price range not including bundle price adjustments.
- Fixed an issue where the last modified date on a setting value was not being updated when the setting value was changed.
- Fixed issue with customer CSV imports treating shared ID as case sensitive in PostgreSQL.
- Removed unused
/authentication/userendpoint in Cortex. - Fixed equals/hashcode implementation in
IndexNotificationImpl. - When a Cortex item and offer keyword searches return zero results, a fallback fuzzy search is supposed to be attempted. The second search was doing the exact same search as the initial search instead of doing a fuzzy search.
- Fixed an issue with Import/Export where the service could run out of memory when importing large files with a lot of errors. Now, only the first 20 errors are held in memory and displayed in the results.
- Fixed issue in which the Data Sync Webapp would try to send emails even if they were disabled by setting
COMMERCE/SYSTEM/emailEnabledto false. - Addressed several split package warnings in Cortex.
- Updated the Data Population
reset-dbfunctionality in MySQL to use thedata.population.databasenameproperty instead of thedata.population.schemaname. - Replaced the custom
ep-tycho-versions-pluginwith the standardtycho-maven-pluginin theset-ep-versions.shscript. - Changed all references to the P2 repositories at
http://download.eclipse.orgwithhttps://download.eclipse.org. - Moved all dependency version definitions to
bill-of-materials/pom.xml. - Moved all plugin version definitions to the top-level
pom.xml. - Fixed issue where an untracked file (
ruleUpdate.properties) was left in the Git source folder after running a build with tests enabled. - Changed
ep-test-applicationdependencies to test scope to ensure that test artifacts don't end up in the compiled WAR files. - Updated Checkstyle plugin configuration to remove use of deprecated
sourceDirectoryparameter that appeared as a warning in the build output. - Fixed PostgreSQL initialization scripts so that they work properly when a low-privilege database user is specified in the
data.population.usernamedata population parameter. - Removed the Commerce Manager reactors from
mvnmin.xml, which are no longer required after the Tycho 4 upgrade.
Additional Commerce Manager fixes
- Fixed Commerce Manager build failure that appears as "bundle org.eclipse.equinox.p2.repository is not started" error.
- Fixed issue where scroll bar doesn't appear as expected after adding new promotion conditions or actions.
- Fixed Commerce Manager to allow orders in the
CREATEDstate to be canceled. - Added ability to use quotes to request an exact match on each individual word when searching for products and skus in Commerce Manager.
- Fixed search error that can occur if a Commerce Manager search field contains
ORorAND. - Fixed issue with currency codes being duplicated in the currency drop-down on shopping cart promotions.
- Fixed an error that could appear when doing search operations in Commerce Manager if the
COMMERCE/SEARCH/boostssystem configuration setting was specified. - Fixed issue with fields not properly being disabled on the coupon assignment page of the shopping cart promotion wizard.
- Fixed issue with the "Assign All Stores" option being disabled in some cases when copying a shopping cart promotion.
- Improved messaging around where a generic "A system error has occurred" error that appeared if a user attempts to delete a product sku that is in use on an order.
- Fixed issue where price list drop-down in Commerce Manager product editor was empty unless user had access to all catalogs.
- Fixed issue with sorting accounts by business number where duplicate records were appearing.
- Fixed issue where buyer admins see customers from other stores when associating buyers to an account by email address.
- Fixed issue with selected disabled radio buttons and checkboxes being invisible on the shopping cart promotion wizard.
- Fixed issue with Commerce Manager initialization that can occur if several initial requests are received concurrently.
Additional Performance fixes
-
Refactored
InventoryFlowServiceImplso that product skus are passed as parameters and unnecessary database lookups can be avoided. -
Refactored
ProductInventoryShoppingServiceImplto prevent inventory lookup for all skus in a multi-sku product when checking inventory for a single sku. -
Added logic to avoid creating unnecessary shopper and shopping cart records when the
x-ep-account-shared-idheader is set in Cortex. -
Refactored
AbstractShoppingItemImplto eliminate unnecessary queries to update cart item last modified date (i.e.UPDATE TCARTITEM SET LAST_MODIFIED_DATE = ? WHERE UIDPK = ?) when persisting the shopping cart. -
Removed the
TSHOPPINGITEMRECURRINGPRICEtable and changed the relationship fromShoppingItemImpltoShoppingItemRecurringPriceImplfrom persisted to transient. Since pricing is recalculated each time the shopping cart is loaded, there's no reason to persist recurring prices in the database. This allows us to eliminate the following unnecessary queries:SELECT t0.UIDPK, t0.GUID, t0.FREQ_AMOUNT, t0.FREQ_UNIT, t0.PAYMENT_SCHEDULE_NAME, t0.DURATION_AMOUNT, t0.DURATION_UNIT, t0.LIST_UNIT_PRICE, t0.PROMO_UNIT_PRICE, t0.SALE_UNIT_PRICE FROM TSHOPPINGITEMRECURRINGPRICE t0 WHERE t0.CARTITEM_UID = ? -
Removed the JPA relationship from
ProductImpltoProductTypeImpl. Product type is now loaded only on-demand if theProduct#getProductTypemethod is called. We also improved caching of product types inCachingProductTypeDaoImpl. The main benefit of this change is that the product cache uses 30-60% less memory. -
Improved performance of the
wishlistmembershiplink by eliminating duplicate shopper and customer queries. -
Added a 60 second cache around inventory lookups done by Cortex during add-to-cart operations and availability requests.
- This means that for high demand physical products, these products might appear available or be permitted to be added to cart for up to a minute after they run out of stock.
- However, the final inventory lookup at checkout is not cached, so shoppers will be blocked from checking out products that have run out of inventory.
-
Refactored the
core-changelog-2021-01-data-fields-as-json-clob.xmlLiquibase changeset to make it run 20-30X faster on PostgreSQL databases. -
Changed
sortattributeslink to static instead of conditional to remove unnecessary extra product search when using theoffersearchresource. -
Fixed product lookup cache population bug that can lead to unnecessary database queries.
-
Added a database index on the
nameandstate_codefields of theTCHANGESETtable to address performance issue in the Automated Imports Accelerator.
Additional Test fixes
- Fixed intermittent failure in the
Promotion Search With Quotes.Search for promotion in store by single name no quotesCucumber test. - Fixed intermittent failure in the
AccessTokenDtoTransformerTest.testTransformToOAuth2AccessTokenunit test. - Fixed intermittent failure in several Cucumber tests that appears as
Unable to find event type [ORDER_RELEASED]. - Fixed intermittent failure in several Selenium tests that appeared as
Error forwarding the new session Empty pool of VM for setup. - Improved reliability of
SarchIndexDefinition#verifyIndexStatusmethod that verifies the Search Index status in Cucumber tests. - Deleted the
commerce-engine/core/ep-core-cucumber-itestsmodule, which only contained a single test of dubious value. - Improved
H2DataSourceInitializerImplto prevent H2 database snapshots from being corrupted when multiple tests are run concurrently. - Modified the
webapp-smoketestsmodule to validate services using liveness healthcheck instead of readiness healthcheck, and removed an unnecessary dependency on htmlunit. - Fixed issue where parent-widget-id and widget-type attributes on a table row were not properly set after a table is updated. This could lead to Selenium test issues.
- Several Cucumber tests and the Webapp Smoke tests module start Self-Managed Commerce services using the Cargo Plugin. These tests instructed the services to listen for JMX requests on pre-defined ports. These ports were sometimes used by other Operating System services which led to "port in use" exceptions. The JMX parameters have now been removed so that the services will no longer listen on these ports.
- Modified Performance Insights so that Core Request-Scoped Caching is disabled when these tests are executed to ensure that it doesn't hide performance issues.
Supported technology updates
Self-Managed Commerce 8.6.0 is compatible with the following Elastic Path releases:
| Elastic Path Component | Compatibility |
|---|---|
| Extension Point Framework | Extension Point Framework compatibility matrix |
| CloudOps for Kubernetes | CloudOps for Kubernetes compatibility matrix |
| Self-Managed Commerce Docker | Self-Managed Commerce Docker compatibility matrix |
For more information, see Supported Technologies.
Dependency changes
Many dependencies were updated as part of Self-Managed Commerce 8.6.0. The highlights are shown below:
- Upgraded ActiveMQ from 5.16.5 to 5.17.6 to address CVE-2023-46604 and CVE-2023-46604.
- Upgraded Apache Shiro from 1.9.1 to 1.13.0 to address CVE-2023-34478 and CVE-2023-46749.
- Upgraded Apache SOLR from 8.11.1 to 9.4.1 to address several CVEs.
- Upgraded certified Tomcat version from 9.0.50 to 9.0.85 to address several CVEs.
- Upgraded Drools from 7.6 to 7.74.1 to address CVE-2022-1415.
- Upgraded h2 from 2.1.214 to 2.2.224 to address CVE-2022-45868.
- Upgraded Liquibase from 4.8.0 to 4.27.0 to support new functionality.
- Upgraded Logback from 1.2.10 to 1.2.13 to address CVE-2023-6481.
- Upgraded Maven Failsafe Plugins and Maven Surefire Plugins from 2.22.2 to 3.1.2 to support new functionality.
- Upgraded pf4j from 3.6.0 to 3.10.0 to address CVE-2023-40828.
- Upgraded Spring Framework from 5.3.26 to 5.3.34 to address CVE-2023-20863, CVE-2024-2225, CVE-2024-22243, CVE-2024-22262.
The complete list of all library dependency updates can be seen in the table below:
| Library | Change |
|---|---|
| activemq-broker-5.17.5.jar | Version changed from 5.16.5 |
| activemq-client-5.17.6.jar | Version changed from 5.17.5 |
| activemq-jms-pool-5.17.6.jar | Version changed from 5.17.5 |
| activemq-kahadb-store-5.17.5.jar | Removed |
| activemq-mqtt-5.17.6.jar | Added |
| activemq-openwire-legacy-5.17.5.jar | Version changed from 5.16.5 |
| activemq-pool-5.17.6.jar | Version changed from 5.17.5 |
| activemq-spring-5.16.7.jar | Version changed from 5.16.5 |
| activemq-web-console-5.17.6.war | Version changed from 5.17.5 |
| ant-1.10.14.jar | Version changed from 1.7.1 |
| ant-launcher-1.10.14.jar | Version changed from 1.7.1 |
| antisamy-1.7.5.jar | Version changed from 1.6.7 |
| antlr4-runtime-4.8.jar | Version changed from 4.5.1-1 |
| antlr4-runtime-4.7.1.jar | Removed |
| apache-el-9.0.83.1.jar | Version changed from 8.5.70 |
| apache-jsp-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| apache-jsp-9.0.83.1.jar | Version changed from 8.5.70 |
| apache-jstl-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| api-asn1-api-2.1.5.jar | Added |
| api-asn1-ber-2.1.5.jar | Added |
| api-i18n-2.1.5.jar | Added |
| api-ldap-model-2.1.5.jar | Added |
| api-util-2.1.5.jar | Added |
| apiguardian-api-1.1.0.jar | Removed |
| asm-7.2.jar | Version changed from 8.0.1 |
| asm-analysis-7.2.jar | Added |
| asm-commons-7.2.jar | Version changed from 8.0.1 |
| asm-tree-7.2.jar | Added |
| audience-annotations-0.12.0.jar | Version changed from 0.5.0 |
| avatica-core-1.18.0.jar | Removed |
| awaitility-3.1.6.jar | Version changed from 2.0.0 |
| batik-constants-1.17.jar | Version changed from 1.14 |
| batik-css-1.17.jar | Version changed from 1.14 |
| batik-i18n-1.17.jar | Version changed from 1.14 |
| batik-shared-resources-1.17.jar | Version changed from 1.14 |
| batik-util-1.17.jar | Version changed from 1.14 |
| caffeine-3.1.8.jar | Version changed from 2.9.2 |
| calcite-core-1.27.0.jar | Removed |
| calcite-linq4j-1.27.0.jar | Removed |
| camel-activemq-3.14.10.jar | Version changed from 3.14.6 |
| camel-api-3.14.10.jar | Version changed from 3.14.6 |
| camel-attachments-3.14.10.jar | Version changed from 3.14.6 |
| camel-base-3.14.10.jar | Version changed from 3.14.6 |
| camel-base-engine-3.14.10.jar | Version changed from 3.14.6 |
| camel-bean-3.14.10.jar | Version changed from 3.14.6 |
| camel-browse-3.14.10.jar | Version changed from 3.14.6 |
| camel-cloud-3.14.10.jar | Version changed from 3.14.6 |
| camel-cluster-3.14.10.jar | Version changed from 3.14.6 |
| camel-controlbus-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-engine-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-languages-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-model-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-processor-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-reifier-3.14.10.jar | Version changed from 3.14.6 |
| camel-core-xml-3.14.10.jar | Version changed from 3.14.6 |
| camel-dataformat-3.14.10.jar | Version changed from 3.14.6 |
| camel-dataset-3.14.10.jar | Version changed from 3.14.6 |
| camel-direct-3.14.10.jar | Version changed from 3.14.6 |
| camel-directvm-3.14.10.jar | Version changed from 3.14.6 |
| camel-file-3.14.10.jar | Version changed from 3.14.6 |
| camel-groovy-3.14.10.jar | Version changed from 3.14.6 |
| camel-health-3.14.10.jar | Version changed from 3.14.6 |
| camel-http-base-3.14.10.jar | Version changed from 3.14.6 |
| camel-http-common-3.14.10.jar | Version changed from 3.14.6 |
| camel-jackson-3.14.10.jar | Version changed from 3.14.6 |
| camel-jaxb-3.14.10.jar | Version changed from 3.14.6 |
| camel-jms-3.14.10.jar | Version changed from 3.14.6 |
| camel-jsonpath-3.14.10.jar | Version changed from 3.14.6 |
| camel-language-3.14.10.jar | Version changed from 3.14.6 |
| camel-log-3.14.10.jar | Version changed from 3.14.6 |
| camel-mail-3.14.10.jar | Version changed from 3.14.6 |
| camel-management-3.14.10.jar | Added |
| camel-management-api-3.14.10.jar | Version changed from 3.14.6 |
| camel-mock-3.14.10.jar | Version changed from 3.14.6 |
| camel-ref-3.14.10.jar | Version changed from 3.14.6 |
| camel-rest-3.14.10.jar | Version changed from 3.14.6 |
| camel-saga-3.14.10.jar | Version changed from 3.14.6 |
| camel-scheduler-3.14.10.jar | Version changed from 3.14.6 |
| camel-seda-3.14.10.jar | Version changed from 3.14.6 |
| camel-servlet-3.14.10.jar | Version changed from 3.14.6 |
| camel-spring-3.14.10.jar | Version changed from 3.14.6 |
| camel-spring-xml-3.14.10.jar | Version changed from 3.14.6 |
| camel-stub-3.14.10.jar | Version changed from 3.14.6 |
| camel-support-3.14.10.jar | Version changed from 3.14.6 |
| camel-swagger-java-3.14.10.jar | Version changed from 3.14.6 |
| camel-test-3.14.10.jar | Version changed from 3.14.6 |
| camel-test-spring-3.14.10.jar | Version changed from 3.14.6 |
| camel-timer-3.14.10.jar | Version changed from 3.14.6 |
| camel-tooling-model-3.14.10.jar | Version changed from 3.14.6 |
| camel-util-3.14.10.jar | Version changed from 3.14.6 |
| camel-util-json-3.14.10.jar | Version changed from 3.14.6 |
| camel-validator-3.14.10.jar | Version changed from 3.14.6 |
| camel-vm-3.14.10.jar | Version changed from 3.14.6 |
| camel-xml-io-util-3.14.10.jar | Version changed from 3.14.6 |
| camel-xml-jaxb-3.14.10.jar | Version changed from 3.14.6 |
| camel-xml-jaxp-3.14.10.jar | Version changed from 3.14.6 |
| camel-xpath-3.14.10.jar | Version changed from 3.14.6 |
| camel-xslt-3.14.10.jar | Version changed from 3.14.6 |
| cglib-nodep-2.1_3.jar | Removed |
| cglib-nodep-3.1.jar | Removed |
| checker-qual-3.12.0.jar | Removed |
| checker-qual-3.33.0.jar | Version changed from 3.10.0 |
| classmate-1.5.1.jar | Version changed from 1.3.4 |
| com.ibm.icu.base-58.2.0.v20170418-1837.eclipse-plugin | Removed |
| commons-compiler-3.0.9.jar | Removed |
| commons-fileupload-1.4.jar | Added |
| commons-pool2-2.4.2.jar | Removed |
| commons-pool2-2.11.1.jar | Removed |
| curator-client-2.13.0.jar | Removed |
| curator-framework-2.13.0.jar | Removed |
| curator-recipes-2.13.0.jar | Removed |
| dec-0.1.2.jar | Removed |
| disruptor-3.4.2.jar | Removed |
| drools-compiler-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| drools-core-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| drools-core-dynamic-7.74.1.Final.jar | Added |
| drools-core-reflective-7.74.1.Final.jar | Added |
| drools-ecj-7.74.1.Final.jar | Added |
| drools-mvel-7.74.1.Final.jar | Added |
| ecj-4.4.2.jar | Removed |
| ecj-3.33.0.jar | Version changed from 3.19.0 |
| eigenbase-properties-1.1.5.jar | Removed |
| error_prone_annotations-2.18.0.jar | Version changed from 2.11.0 |
| esapi-2.5.3.1.jar | Version changed from 2.3.0.0 |
| esri-geometry-api-2.2.0.jar | Removed |
| guava-32.0.1-jre.jar | Version changed from 31.1-jre |
| h2-2.2.224.jar | Version changed from 2.1.214 |
| hawtdispatch-1.22.jar | Version changed from 1.11 |
| hawtdispatch-transport-1.22.jar | Version changed from 1.11 |
| hibernate-validator-6.2.0.Final.jar | Version changed from 6.0.20.Final |
| hppc-0.9.1.jar | Version changed from 0.8.1 |
| hsqldb-2.3.2.jar | Removed |
| htmlunit-2.70.0.jar | Removed |
| htmlunit-core-js-2.70.0.jar | Removed |
| htmlunit-cssparser-1.14.0.jar | Removed |
| htmlunit-xpath-2.70.0.jar | Removed |
| htrace-core4-4.1.0-incubating.jar | Removed |
| http2-client-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| http2-common-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| http2-hpack-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| http2-http-client-transport-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| http2-server-9.4.44.v20210927.jar | Removed |
| httpclient5-5.3.1.jar | Version changed from 5.1.3 |
| httpcore5-5.2.4.jar | Version changed from 5.1.3 |
| httpcore5-h2-5.2.4.jar | Version changed from 5.1.3 |
| imap-1.5.6.jar | Version changed from 1.5.2 |
| j2objc-annotations-2.8.jar | Version changed from 1.3 |
| jackson-annotations-2.16.1.jar | Version changed from 2.13.4 |
| jackson-core-2.16.1.jar | Version changed from 2.13.4 |
| jackson-databind-2.16.1.jar | Version changed from 2.13.4 |
| jackson-dataformat-cbor-2.16.1.jar | Added |
| jackson-dataformat-smile-2.16.1.jar | Version changed from 2.12.3 |
| jackson-datatype-jsr310-2.16.1.jar | Version changed from 2.13.4 |
| jackson-jaxrs-base-2.16.1.jar | Version changed from 2.13.4 |
| jackson-jaxrs-json-provider-2.16.1.jar | Version changed from 2.13.4 |
| jackson-module-jaxb-annotations-2.16.1.jar | Version changed from 2.13.4 |
| jakarta.el-3.0.4.jar | Added |
| jakarta.servlet.jsp.jstl-api-1.2.7.jar | Added |
| jakarta.transaction-api-1.3.3.jar | Added |
| jakarta.validation-api-2.0.2.jar | Added |
| janino-3.0.9.jar | Removed |
| javax.el-3.0.0.jar | Removed |
| javax.inject-1.0.0.v20091030.eclipse-plugin | Removed |
| jaxb-api-2.3.1.jar | Added |
| jboss-logging-3.4.1.Final.jar | Version changed from 3.3.2.Final |
| jcip-annotations-1.0-1.jar | Added |
| jersey-container-jetty-http-2.39.1.jar | Added |
| jersey-entity-filtering-2.39.1.jar | Added |
| jersey-media-json-jackson-2.39.1.jar | Added |
| jersey-server-2.39.1.jar | Added |
| jetty-alpn-client-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-alpn-java-client-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-annotations-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-client-9.4.50.v20221201.jar | Removed |
| jetty-client-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-http-10.0.20.jar | Version changed from 9.4.50.v20221201 |
| jetty-io-10.0.20.jar | Version changed from 9.4.50.v20221201 |
| jetty-jaas-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-jndi-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-plus-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-runner-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| jetty-schemas-4.0.3.jar | Version changed from 3.1.2 |
| jetty-security-10.0.20.jar | Added |
| jetty-server-10.0.20.jar | Added |
| jetty-servlet-10.0.20.jar | Added |
| jetty-servlet-api-4.0.6.jar | Added |
| jetty-slf4j-impl-10.0.20.jar | Added |
| jetty-util-9.4.51.v20230217.jar | Added |
| jetty-util-10.0.20.jar | Added |
| jetty-webapp-10.0.20.jar | Added |
| jetty-xml-10.0.20.jar | Added |
| jjwt-api-0.10.5.jar | Removed |
| jjwt-impl-0.10.5.jar | Removed |
| jjwt-jackson-0.10.5.jar | Removed |
| jose4j-0.6.5.jar | Removed |
| json-20231013.jar | Version changed from 20220924 |
| json-path-2.9.0.jar | Version changed from 2.6.0 |
| jsoup-1.15.3.jar | Version changed from 1.8.3 |
| jstl-1.2.jar | Removed |
| jstl-1.1.2.jar | Removed |
| junit-4.13.1.jar | Version changed from 4.12 |
| kerb-core-1.0.1.jar | Removed |
| kerb-util-1.0.1.jar | Removed |
| kerby-asn1-1.0.1.jar | Removed |
| kerby-pkix-1.0.1.jar | Removed |
| kie-api-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| kie-internal-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| kie-memory-compiler-7.74.1.Final.jar | Added |
| kie-soup-commons-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| kie-soup-maven-support-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| kie-soup-project-datamodel-api-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| kie-soup-project-datamodel-commons-7.74.1.Final.jar | Version changed from 7.6.0.Final |
| kie-soup-xstream-7.74.1.Final.jar | Added |
| liquibase-core-4.27.0.jar | Version changed from 4.8.0 |
| log4j-layout-template-json-2.16.0.jar | Removed |
| logback-classic-1.2.13.jar | Version changed from 1.2.10 |
| logback-core-1.2.13.jar | Version changed from 1.2.10 |
| lucene-analysis-common-9.8.0.jar | Added |
| lucene-analysis-kuromoji-9.8.0.jar | Added |
| lucene-analysis-nori-9.8.0.jar | Added |
| lucene-analysis-phonetic-9.8.0.jar | Added |
| lucene-analyzers-common-8.11.1.jar | Removed |
| lucene-analyzers-kuromoji-8.11.1.jar | Removed |
| lucene-analyzers-nori-8.11.1.jar | Removed |
| lucene-analyzers-phonetic-8.11.1.jar | Removed |
| lucene-backward-codecs-9.8.0.jar | Version changed from 8.11.1 |
| lucene-classification-9.8.0.jar | Version changed from 8.11.1 |
| lucene-codecs-9.8.0.jar | Version changed from 8.11.1 |
| lucene-core-9.8.0.jar | Version changed from 8.11.1 |
| lucene-expressions-9.8.0.jar | Version changed from 8.11.1 |
| lucene-grouping-9.8.0.jar | Version changed from 8.11.1 |
| lucene-highlighter-9.8.0.jar | Version changed from 8.11.1 |
| lucene-join-9.8.0.jar | Version changed from 8.11.1 |
| lucene-memory-9.8.0.jar | Version changed from 8.11.1 |
| lucene-misc-9.8.0.jar | Version changed from 8.11.1 |
| lucene-queries-9.8.0.jar | Version changed from 8.11.1 |
| lucene-queryparser-9.8.0.jar | Version changed from 8.11.1 |
| lucene-sandbox-9.8.0.jar | Version changed from 8.11.1 |
| lucene-spatial-extras-9.8.0.jar | Version changed from 8.11.1 |
| lucene-spatial3d-9.8.0.jar | Version changed from 8.11.1 |
| lucene-suggest-9.8.0.jar | Version changed from 8.11.1 |
| metrics-jetty9-4.1.5.jar | Removed |
| metrics-jmx-4.2.21.jar | Version changed from 4.1.5 |
| metrics-jvm-4.2.21.jar | Version changed from 4.1.5 |
| mina-core-2.2.3.jar | Added |
| mqtt-client-1.16.jar | Version changed from 1.3 |
| mvel2-2.4.13.Final.jar | Version changed from 2.4.0.Final |
| mysql-connector-j-8.2.0.jar | Added |
| mysql-connector-java-8.0.30.jar | Removed |
| neko-htmlunit-3.11.1.jar | Version changed from 2.24 |
| nekohtml-1.9.16.jar | Removed |
| netty-buffer-4.1.105.Final.jar | Version changed from 4.1.68.Final |
| netty-codec-4.1.105.Final.jar | Version changed from 4.1.68.Final |
| netty-common-4.1.105.Final.jar | Version changed from 4.1.68.Final |
| netty-handler-4.1.68.Final.jar | Removed |
| netty-handler-4.1.105.Final.jar | Version changed from 4.1.50.Final |
| netty-resolver-4.1.105.Final.jar | Version changed from 4.1.68.Final |
| netty-tcnative-boringssl-static-2.0.61.Final-linux-aarch_64.jar | Added |
| netty-tcnative-boringssl-static-2.0.61.Final-linux-x86_64.jar | Added |
| netty-tcnative-boringssl-static-2.0.61.Final-osx-aarch_64.jar | Added |
| netty-tcnative-boringssl-static-2.0.61.Final-osx-x86_64.jar | Added |
| netty-tcnative-boringssl-static-2.0.61.Final-windows-x86_64.jar | Added |
| netty-tcnative-boringssl-static-2.0.61.Final.jar | Added |
| netty-tcnative-classes-2.0.61.Final.jar | Added |
| netty-transport-4.1.105.Final.jar | Version changed from 4.1.68.Final |
| netty-transport-classes-epoll-4.1.105.Final.jar | Added |
| netty-transport-native-epoll-4.1.50.Final.jar | Removed |
| netty-transport-native-epoll-4.1.68.Final.jar | Removed |
| netty-transport-native-epoll-4.1.105.Final-linux-x86_64.jar | Added |
| netty-transport-native-unix-common-4.1.105.Final.jar | Version changed from 4.1.68.Final |
| nimbus-jose-jwt-9.37.2.jar | Added |
| objenesis-2.6.jar | Version changed from 2.1 |
| opencsv-5.9.jar | Added |
| openjpa-3.2.2-ep1.4.jar | Version changed from 3.2.2-ep1.3 |
| org.apache.servicemix.bundles.antlr-3.5.2_1.jar | Added |
| pf4j-3.10.0.jar | Version changed from 3.6.0 |
| poi-4.1.1.jar | Version changed from 4.0.1 |
| postgresql-42.4.4.jar | Version changed from 42.3.3 |
| protobuf-java-3.16.3.jar | Version changed from 3.11.0 |
| re2j-1.2.jar | Removed |
| rrd4j-3.5.jar | Removed |
| salvation2-3.0.1.jar | Removed |
| semver4j-5.2.2.jar | Added |
| shiro-cache-1.13.0.jar | Version changed from 1.9.1 |
| shiro-config-core-1.13.0.jar | Version changed from 1.9.1 |
| shiro-config-ogdl-1.13.0.jar | Version changed from 1.9.1 |
| shiro-core-1.13.0.jar | Version changed from 1.9.1 |
| shiro-crypto-cipher-1.13.0.jar | Version changed from 1.9.1 |
| shiro-crypto-core-1.13.0.jar | Version changed from 1.9.1 |
| shiro-crypto-hash-1.13.0.jar | Version changed from 1.9.1 |
| shiro-event-1.13.0.jar | Version changed from 1.9.1 |
| shiro-lang-1.13.0.jar | Version changed from 1.9.1 |
| simplemagic-1.17.jar | Added |
| slf4j-log4j12-1.7.25.jar | Removed |
| snakeyaml-2.2.jar | Added |
| snappy-java-1.1.10.5.jar | Version changed from 1.1.7.6 |
| solr-api-9.4.1.jar | Added |
| solr-core-9.4.1.jar | Version changed from 8.11.1 |
| solr-scripting-9.4.1.jar | Added |
| solr-solrj-9.4.1.jar | Version changed from 8.11.1 |
| solr-solrj-streaming-9.4.1.jar | Added |
| solr-solrj-zookeeper-9.4.1.jar | Added |
| spatial4j-0.8.jar | Version changed from 0.7 |
| spring-aop-5.3.34.jar | Version changed from 5.3.26 |
| spring-beans-5.3.34.jar | Version changed from 5.3.26 |
| spring-context-5.3.34.jar | Version changed from 5.3.26 |
| spring-context-support-5.3.34.jar | Version changed from 5.3.26 |
| spring-core-5.3.34.jar | Version changed from 5.3.26 |
| spring-expression-5.3.34.jar | Version changed from 5.3.26 |
| spring-jcl-5.3.34.jar | Version changed from 5.3.26 |
| spring-jdbc-5.3.34.jar | Version changed from 5.3.26 |
| spring-jms-5.3.34.jar | Version changed from 5.3.26 |
| spring-messaging-5.3.34.jar | Version changed from 5.3.26 |
| spring-orm-5.3.34.jar | Version changed from 5.3.26 |
| spring-security-config-5.8.7.jar | Version changed from 5.8.5 |
| spring-security-core-5.8.7.jar | Version changed from 5.8.5 |
| spring-security-crypto-5.8.7.jar | Version changed from 5.8.5 |
| spring-security-web-5.8.7.jar | Version changed from 5.8.5 |
| spring-test-5.3.34.jar | Version changed from 5.3.26 |
| spring-tx-5.3.34.jar | Version changed from 5.3.26 |
| spring-web-5.3.34.jar | Version changed from 5.3.26 |
| ST4-4.0.8.jar | Added |
| standard-1.1.2.jar | Removed |
| stax2-api-4.2.2.jar | Added |
| swagger-annotations-2.2.17.jar | Added |
| websocket-api-9.4.44.v20210927.jar | Removed |
| websocket-api-9.4.50.v20221201.jar | Removed |
| websocket-client-9.4.44.v20210927.jar | Removed |
| websocket-client-9.4.50.v20221201.jar | Removed |
| websocket-common-9.4.44.v20210927.jar | Removed |
| websocket-common-9.4.50.v20221201.jar | Removed |
| websocket-core-common-10.0.20.jar | Added |
| websocket-core-server-10.0.20.jar | Added |
| websocket-jetty-api-10.0.20.jar | Added |
| websocket-jetty-common-10.0.20.jar | Added |
| websocket-jetty-server-10.0.20.jar | Added |
| websocket-server-9.4.44.v20210927.jar | Removed |
| websocket-servlet-10.0.20.jar | Version changed from 9.4.44.v20210927 |
| woodstox-core-6.5.1.jar | Version changed from 6.2.4 |
| xbean-spring-4.22.jar | Version changed from 4.21 |
| xercesImpl-2.12.0.jar | Removed |
| xmlgraphics-commons-2.9.jar | Version changed from 2.6 |
| xom-1.2.10.jar | Removed |
| zookeeper-3.9.2.jar | Version changed from 3.6.2 |
| zookeeper-jute-3.9.2.jar | Version changed from 3.6.2 |
Upgrade notes
The upgrading Elastic Path guide provides general instructions on upgrading Elastic Path projects.
ShopperReadOnly annotation
A new annotation has been added to the platform called @ShopperReadOnly. This annotation should be added to all JPA domain classes for tables that should never be modified by Cortex. For example, shoppers should not be able to modify catalog, product, setting definition, or payment configuration records.
When this annotation is added to a class, a JPA entity listener in Cortex called ShopperReadOnlyEntityListener is executed on attempts to insert, update, or delete JPA managed entities. This listener will throw an exception if the entity is represented by a JPA entity class with the @ShopperReadOnly annotation. This provides a safeguard to ensure that any logic errors in the code do not allow business data to be modified through the Cortex API.
Additionally, two new PMD rules have been added that look for the @ShopperReadOnly annotation to ensure that JPA entity classes are configured properly. These rules are described in the sections below.
Ensure Transactional Entities have the JPA data cache disabled
This rule ensures that the JPA data cache is disabled for JPA domain classes that are expected to be modified in Cortex.
If a class has an @Entity annotation, does not have a @ShopperReadOnly annotation, and does not have a @DataCache(enabled = false) annotation, a build-time PMD failure will be reported:
Commerce transaction JPA classes must be read-only or have data cache disabled to avoid concurrent modification issues
This failure should be resolved by adding the @DataCache(enabled = false) annotation to the class, or adding the @ShopperReadOnly annotation to the class if it should not be modified by Cortex.
Ensure Transactional Entities use table generator with high allocation size
This rule ensures that the table generator for JPA domain classes that are expected to be modified in Cortex have the allocation size set to HIGH_CONCURRENCY_ALLOCATION_SIZE. This is a performance optimization that prevents unnecessary queries against the JPA_GENERATED_KEYS table.
If a class has an @Entity annotation, does not have a @ShopperReadOnly annotation, and has a @TableGenerator annotation on any method that does not have the allocationSize = HIGH_CONCURRENCY_ALLOCATION_SIZE attribute set, a build-time PMD failure will be reported:
Commerce transaction JPA classes with table generators must be read-only or use high allocation size to ensure performance
This failure should be resolved by adding the allocationSize = HIGH_CONCURRENCY_ALLOCATION_SIZE attribute to the @TableGenerator annotation on the class, or adding the @ShopperReadOnly annotation to the class if it should not be modified by Cortex.
Cortex API change: Payment instrument selection
As part of the Split Payments feature, the behaviour of payment instrument selections has changed that may affect API clients. When a payment instrument is selected, any currently selected payment instruments are no longer automatically deselected because multiple payment instruments can now be selected on a cart order.
A payment instrument can be selected on a cart order in several ways:
- A client manually selects an existing payment instrument on the cart order by following a
paymentinstrumentselector-->choicelink on the cart order and posts to theselectactionlink. - A client creates a new payment instrument on the cart order by following a
paymentmethodinfo-->element-->paymentinstrumentformlink on the cart order and posts to thecreatepaymentinstrumentactionlink. - A client creates the first payment instrument on the user's profile by following a
paymentmethods-->element-->paymentinstrumentformlink on the shopper or account profile and posts to thecreatepaymentinstrumentactionlink.
Commerce Engine changes
- The
getUidPkIntmethod was removed from theProductinterface. Use thegetUidPkmethod instead. - The unused
WishListService#shareWithListmethod has been removed. - Cleaned up duplicate
com.h2database:h2dependency definition inep-test-application. - Removed several unused classes from the
ep-coremodule:SeoUrlBuilderImplBreadcrumbsImplSearchRequestImplSearchResultImplAdvancedSearchRequestImplCatalogViewRequestCatalogViewResultSfSearchLogImplShopperBrowsingActivityViewHistoryImplViewHistoryProductImplProductXmlServiceImplSearchServiceImpl
- The
RandomGuidImplclass has been removed. UseUUID#randomUUIDinstead. - The
JpaAdaptorOfSkuOptionValueImplclass has been renamed toProductSkuOptionValueImplto improve clarity. - All Groovy dependencies have been removed from
ep-core. This includes themaven-compiler-pluginconfiguration for compiling Groovy classes. All remaining unused classes for dynamically rendering Groovy scripts have also been removed. - All
hsqldbdependencies have been removed, and all tests have been refactored to useh2. - A separate PMD rule configuration is used for integration test modules, which excludes a number of checks that are normally executed on production modules. Some of those exclusions have now been removed, increasing the number of checks that are run on integration test modules. The following checks have been enabled:
- AvoidFieldNameMatchingMethodName
- AvoidFieldNameMatchingTypeName
- CompareObjectsWithEquals
- FinalFieldCouldBeStatic
- IfElseStmtsMustUseBraces
- IfStmtsMustUseBraces
- ImportFromSamePackage
- PackageCase
- SuspiciousConstantFieldName
- UnnecessaryFullyQualifiedName
- UnusedFormalParameter
- UnusedImports
- UnusedLocalVariable
- UnusedPrivateField
- UnusedPrivateMethod
- UseEqualsToCompareStrings
- Consolidated duplicate
EmailValidatorclasses.- The
com.elasticpath.commons.validator.impl.EpEmailValidatorclass has been removed. - Custom code using the removed
com.elasticpath.commons.validator.impl.EpEmailValidatorclass or the deprecatedorg.apache.commons.validator.EmailValidatorclass should useorg.apache.commons.validator.routines.EmailValidatorinstead.
- The
- The deprecated
solr.LRUCachefilter cache references in the*.config.xmlfiles in theep-searchmodule have been replaced with the updatedsolr.search.CaffeineCacheclass. - The inventory allocation functionality in the
UpdateOrderCheckoutActionclass was moved to a new checkout action class:AllocateInventoryCheckoutAction. - Service class caching wrappers for entities with a time range (
CachingRuleServiceImpl,CachingPriceListAssignmentServiceImpl, andCachingProductAssociationServiceImpl) now make use of the newTimeIntervalCacheclass which ensures that the cache remains efficient and valid results are returned for these time-sensitive entities. - Unused service methods were removed:
CouponDao#doesCouponCodeOnlyExistForThisRuleGuidand the associatedCOUPON_CODES_BY_COUPON_CODE_NOT_RULE_GUIDnamed query.CouponUsageDao#findByCodeand the associatedCOUPON_USAGE_FIND_BY_COUPON_CODEnamed query.
- Several caches were renamed to improve consistency:
cachingAttributesByProfileCache->attributesByProfileCachecachingAttributeServiceAttributesCache->attributeServiceAttributesCachecachingAttributeServicefindByKeyCache->attributeServicefindByKeyCachecachingCategoryServiceFindCodeByUidCache->categoryServiceFindCodeByUidCachecachingSolrQueryFactorySearchableAttributeCache->solrQueryFactorySearchableAttributeCache
Commerce Manager changes
- Several unused reporting modules have now been deleted from the source:
com.elasticpath.cmclient:com.elasticpath.cmclient.reporting.stockallocationcom.elasticpath.cmclient:com.elasticpath.cmclient.reporting.registrationcom.elasticpath.cmclient:com.elasticpath.cmclient.reporting.promotiondetailscom.elasticpath.cmclient:com.elasticpath.cmclient.reporting.giftcertificatesummarycom.elasticpath.cmclient:com.elasticpath.cmclient.reporting.lowstockcom.elasticpath.cmclient:com.elasticpath.cmclient.reporting.giftcertificatedetails
Import/Export changes
- The
promotions-->promotion-->availability-->enabledatefield is now required for all promotion imports. This makes Import/Export consistent with the required enable date when creating promotions in Commerce Manager. - Removed the
Pricefield from the Product fields available for doing product exports. Attempting to use this field was causing an error.
Database changes
- Deleted unused setting definition records:
COMMERCE/SEARCH/minimumResultsThresholdCOMMERCE/SEARCH/maximumResultsThresholdCOMMERCE/SEARCH/maximumSuggestionsPerWordCOMMERCE/SEARCH/accuracyCOMMERCE/SYSTEM/CATALOGSYNDICATIONHISTORYCLEANUP/batchSizeCOMMERCE/SYSTEM/CATALOGSYNDICATIONHISTORYCLEANUP/maxHistory
- Deleted unused setting value context records:
COMMERCE/SYSTEM/MESSAGING/CUSTOMERS/channelUriwith contextwishListSharedEmailHander.
- Added new setting definition records:
COMMERCE/SYSTEM/INACTIVECARTSCLEANUPJOB/minAgeCOMMERCE/SYSTEM/MESSAGING/SHOPPINGCARTS/channelUriCOMMERCE/SYSTEM/MESSAGING/SHOPPINGCARTITEMS/channelUriCOMMERCE/SYSTEM/ABANDONEDCARTEVENTS/batchSizeCOMMERCE/SYSTEM/ABANDONEDCARTEVENTS/maxHistoryCOMMERCE/SYSTEM/MESSAGING/CACHE/channelUri
- Added new setting value context records:
COMMERCE/SYSTEM/MESSAGING/ORDERS/channelUriwith contextorderReleaseExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/CUSTOMERS/channelUriwith contextcustomerEventsExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/SHOPPINGCARTS/channelUriwith contextshoppingCartEventsExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/SHOPPINGCARTITEMS/channelUriwith contextshoppingCartItemEventsExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/DOMAIN/deadLetterChannelUriwith contextorderReleaseExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/DOMAIN/deadLetterChannelUriwith contextcustomerEventsExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/DOMAIN/deadLetterChannelUriwith contextshoppingCartEventsExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/DOMAIN/deadLetterChannelUriwith contextshoppingCartItemEventsExtensionHandlerCOMMERCE/SYSTEM/MESSAGING/DOMAIN/channelUriwith contextdomainCacheHandler
- Removed several duplicate database indexes:
I_TBASEAMOUNT_FK_GUIDonTBASEAMOUNT(covered byI_TBASEAMOUNT_OBJECTS)I_CMUSERCATALOG__USER_UIDonTCMUSERCATALOG(covered by the primary key)I_CMUSERPL_USER_UIDonTCMUSERPRICELIST(covered by the primary key)I_CMUSER_USER_UIDonTCMUSERROLEX(covered by the primary key)I_CMUSERSTORE__USER_UIDonTCMUSERSTORE(covered by the primary key)I_CMUSERWH__USER_UIDonTCMUSERWAREHOUSE(covered by the primary key)I_CUSTOMER_TYPEonTCUSTOMER(covered byI_TYPE_LAST_EDIT)I_CUST_STORE_CODEonTCUSTOMER(covered byI_CUSTOMER_STORECODE_OIDCSUBJECT)I_CUSTOMER_SHAREDIDonTCUSTOMER(covered byTCUSTOMER_SHARED_ID_TYPE_UNIQ)I_INVENTORY_WAREHOUSE_UIDonTINVENTORY(covered byTINVENTORY_UNIQUE)I_TPRICEADJUSTMENT_FK_PL_GUIDonTPRICEADJUSTMENT(covered byI_TPRICEADJUSTMENT_KEYS)I_PC_PUIDonTPRODUCTCATEGORY(covered byTPRODUCTCATEGORY_UNIQUE)I_STORE_ASSOCIATE_UIDonTSTOREASSOCIATION(covered by the primary key)I_USERACCOUNTASSOC_USERIDonTUSERACCOUNTASSOCIATION(covered byUSER_CUSTOMER_GUID)
- Added new indexes to improve performance of shopping cart events:
- Added index to
TCARTORDERonBILLING_GUID. - Added index to
TCARTORDERonSHIPPING_ADDRESS_GUID. - Added index to
TSHOPPINGCARTonSTATUS.
- Added index to
- Added new index to improve performance of changeset lookups:
- Added index to
TCHANGESETonNAMEandSTATE_CODE.
- Added index to
- Moved wishlist line items from
TCARTITEMtoTWISHLISTITEM:- Created
TWISHLISTITEMtable. - Copied
TCARTITEMrecords toTWISHLISTITEMwhereWISHLIST_UIDis not null. - Deleted
TCARTITEMrecords whereWISHLIST_UIDis not null. - Dropped
WISHLIST_UIDfield fromTCARTITEMtable.
- Created
- Modified
TCMUSERtable to support OpenID Connect for business users:- Added
OIDC_SUBJECTfield, with unique constraint index. - Changed
USER_NAMEandPASSWORDfields to allow nulls. - Removed unique constraint index on
EMAILfield.
- Added
- Modified
TSHOPPINGITEMRECURRINGPRICEso it's no longer used for shopping items, only order items:- Deleted
TSHOPPINGITEMRECURRINGPRICErecords whereCARTITEM_UIDis not null. - Dropped
CARTITEM_UIDcolumn fromTSHOPPINGITEMRECURRINGPRICEtable.
- Deleted
- Modified
TCARTITEMtable to improve how the parent/child relationship is defined.- Added
PARENT_ITEM_GUIDfield. - Migrated
PARENT_ITEM_UIDvalues to thePARENT_ITEM_GUIDfield (with transformation). - Migrated
CHILD_ITEM_CART_UIDvalues to theSHOPPING_CART_UIDfield. - Changed
SHOPPING_CART_UIDfield to disallow null values. - Dropped
CHILD_ITEM_CART_UIDandPARENT_ITEM_UIDfields. - Added a unique constraint index on the
GUIDfield.
- Added
- Modified
TCARTITEMtable to support "soft deletes":- Added
REMOVEDfield.
- Added
- Modified
TRULEtable to support shopping cart line item promotions.- Added
EVALUATION_OBJECTfield.
- Added
- Modified
TCUSTOMERAUTHENTICATIONtable so that uniqueness is enforced for records with the same username and store code:- Added
REGISTERED_STORE_CODE_UPPERfield toTCUSTOMERAUTHENTICATION. - Migrated
TCUSTOMER.STORE_CODEvalues toTCUSTOMERAUTHENTICATION.REGISTERED_STORE_CODE_UPPER. - Added a unique constraint index on the
USERNAME_UPPERandREGISTERED_STORE_CODE_UPPERfields.
- Added
- Added support for address line 3:
- Added
STREET_3field toTADDRESStable. - Added
STREET_3field toTORDERADDRESStable. - Added
STREET_3field toTWAREHOUSEADDRESStable.
- Added
- Dropped unused tables:
TSFSEARCHLOGTDIGITALASSETAUDITTCATALOGHISTORY
- Changed default value of
COMMERCE/SYSTEM/FILTEREDNAVIGATION/separatorInTokensetting from_to~to reduce likelihood of collisions with existing values. - Added a non-null constraint to the following fields:
TCUSTOMERAUTHENTICATION.USERNAME_UPPER
- If you are using PostgreSQL in your local development environment, the
postgresql-dev-dbprofile in yoursettings.xmlmust now define theepdb.schemanameparameter. To maintain backwards compatibility, set this topublic. See theextensions/maven/settings.xmlfile for a template to use for your local~/.m2/settings.xmlfile.